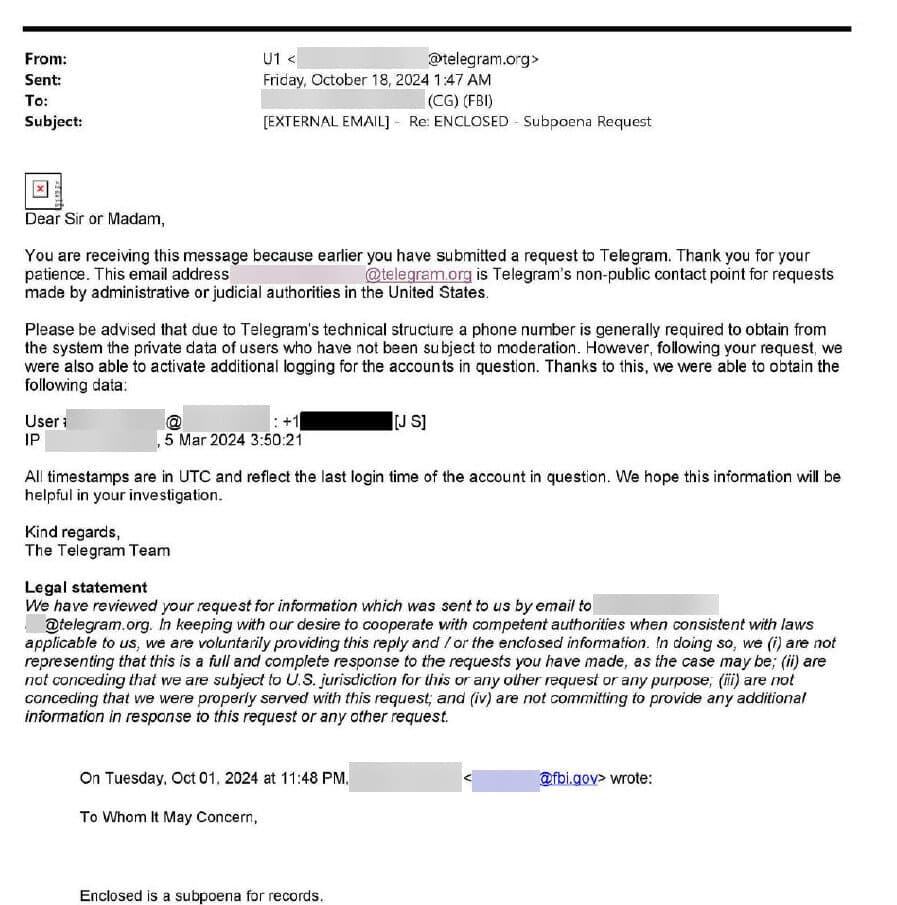
Court filings and an FBI subpoena response now circulating among threat-intelligence researchers show what Telegram hands over to investigators: a user's numeric ID, username, phone number and last-login IP address with a timestamp. In one case, Telegram also switched on additional logging for the targeted accounts to capture that data. The records undercut the belief, common among cybercriminals, that Telegram offers complete anonymity.
Telegram has long been treated by fraudsters, scam call centres and cybercriminal markets as a safe haven. Documents now circulating among threat-intelligence researchers show what the platform actually discloses when US law enforcement asks.
What the records show
A US court filing quotes Telegram's response to an administrative subpoena for one account. Telegram provided:
- User ID: the account's permanent numeric identifier
- Username: the @handle
- Phone number: a US (+1) number linked to the account
- Last login IP address: with the exact date and time of the login, 16 October 2025
 A second document is an email from Telegram to the Federal Bureau of Investigation (FBI), dated 18 October 2024, replying to a subpoena sent on 1 October 2024. It shows how the process works in practice:
- Telegram runs a non-public contact address for requests from US administrative and judicial authorities.
- It says a phone number is generally required to retrieve private data on users who have not been subject to moderation.
- Following the FBI's request, Telegram activated additional logging on the accounts in question. This let it capture the user ID, phone number and an IP address with a last-login timestamp in UTC.
 The fine print
Telegram attached a legal statement to its reply. It says it provides the information voluntarily, "in keeping with our desire to cooperate with competent authorities," and does not concede that it is subject to US jurisdiction or that it was properly served. It also says the reply may not be a full response and that it isn't committing to provide more data in future.
What it does not show
Neither document shows Telegram handing over message content. Telegram says ordinary cloud chats are stored encrypted on its servers, and "Secret Chats" are end-to-end encrypted, so only the two devices involved can read them. What it does disclose is the identifying layer: who is behind an account and where they connected from. That is often enough for investigators to identify a suspect through the mobile carrier or internet provider.
Why it matters
Telegram changed its privacy policy in September 2024, weeks after founder Pavel Durov was detained in France. The updated policy says Telegram may share users' IP addresses and phone numbers in response to valid legal requests in criminal cases, not just terrorism cases as before. The records match that shift, and show Telegram can go further by starting targeted logging on request.
For investigators tracking the Telegram-run romance, investment, task and loan-app scams that feed cyber fraud across South Asia and beyond, the lesson is clear. A phone number and an IP address with a timestamp are often the thread that unravels a network. For criminals, the belief that a Telegram handle guarantees anonymity is badly outdated.