Threat Intelligence: DMCA-Themed Credential Phishing Targeting X (Twitter) Users
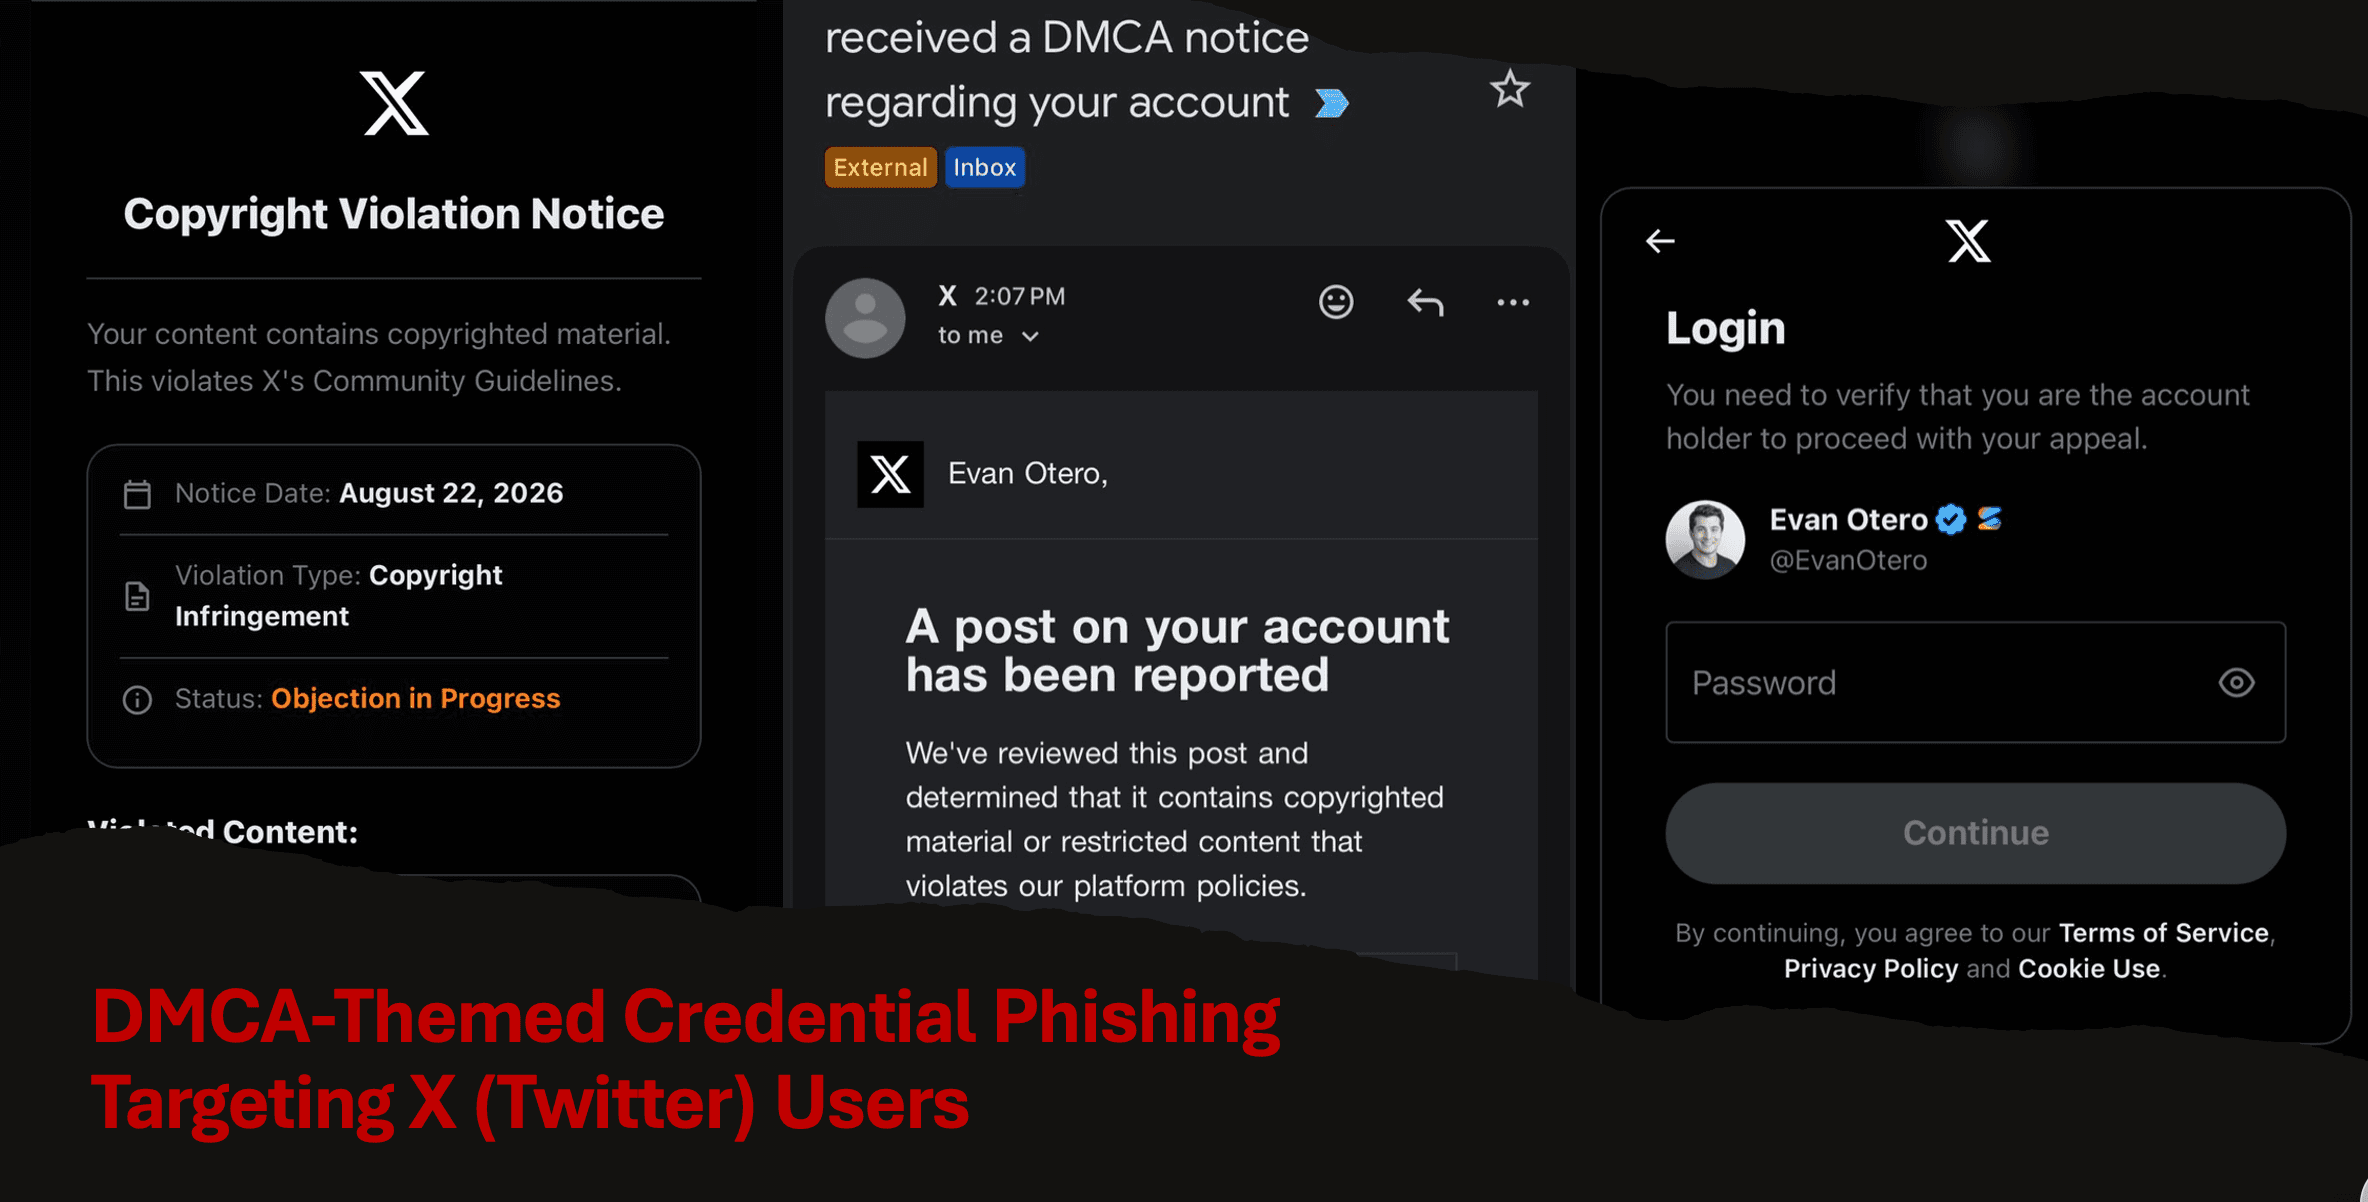
Campaign Focus: contentviolations-x.com and Related -x.com Infrastructure
On 22 August 2026, a Google DeepMind technical staff member publicly disclosed a highly personalized phishing email impersonating an official X (formerly Twitter) DMCA copyright notice.
The lure directed the victim to the newly registered domain contentviolations-x.com, which presented a convincing X-branded “Copyright Violation Notice” page containing a screenshot of the target’s actual recent post.
The page then prompted for account credentials under the guise of submitting an appeal.
This incident forms part of a long-running, industrially scaled phishing campaign that has operated since at least mid-2024.
Operators continuously register lookalike domains ending in -x.com, use JavaScript-driven page rendering to evade static scanners, personalize content with publicly available post data, and harvest credentials for account takeover, commonly followed by crypto scam promotion or further social-engineering attacks.
Campaign Overview and Historical Context
Threat actors have maintained a large portfolio of domains following the pattern *-[content|violation|flagged|policy|status|disputes|recognition|etc]-x.com.
Documented examples include flaggedcontents-x.com, violating-x.com, policyviolation-x.com, recognition-x.com, and dozens of others.
A detailed analysis published in April 2026 identified more than 60 such domains registered since August 2024, many through Turkish registrars (notably Turkticaret.net) and frequently resolving through Cloudflare or Turkish/Hostinger infrastructure.
New domains continue to appear; contentviolations-x.com itself was registered on 12 August 2026, only ten days before the observed email.
The primary objective is credential theft leading to high-value X account compromise.
Compromised accounts are typically used to post crypto giveaways, investment scams, or to further phish followers.
Technical Analysis of the Observed Lure
1. Email Delivery
- Subject line format observed: LEGAL-9354533: We've received a DMCA notice regarding your account
- The message appears in Gmail with an “External” label and is styled to resemble official X correspondence.
- Body text claims a specific post has been reviewed and determined to contain copyrighted or restricted material.
- A realistic screenshot of the target’s own post (including engagement metrics and content disclosures) is embedded.
- Call-to-action links or buttons lead to the phishing domain.
Legitimate X DMCA notices never arrive as unsolicited emails demanding immediate login; official processes occur inside the platform or via designated copyright agent channels.
2. Landing Page Behavior
- Root path (https://contentviolations-x.com/) returns approximately 800 bytes of essentially empty HTML. Content is dynamically constructed client-side via JavaScript. This technique defeats many content-based phishing detectors and URL scanners that score only static page text.
- Once rendered, the page closely clones X’s dark-mode interface:
- Official X logo and typography
- “Copyright Violation Notice” header
- Notice date (matching the email day)
- Violation type: Copyright Infringement
- Status: “Objection in Progress”
- Embedded screenshot of the victim’s exact post
- Subsequent page presents a login form: “You need to verify that you are the account holder to proceed with your appeal,” pre-filled with the target’s display name, handle, and profile picture, requesting only the password.
3. Personalization Engine Attackers scrape public X posts (or use previously compromised data) to embed authentic screenshots and metadata. This significantly increases credibility and reduces the chance a user will dismiss the notice as generic spam. In the observed case the embedded post concerned “Content disclosures – It’s a joke,” matching the victim’s recent activity.
4. Infrastructure Characteristics
- Domains are young (days to weeks old at time of use).
- Heavy reliance on Cloudflare for DNS and CDN.
- JavaScript-heavy rendering + minimal static content = low detection scores on automated scanners.
- Similar historical domains have shown PHP backend errors when parameters are missing (e.g., undefined array keys for username/avatar), indicating templated kits that expect a username or session parameter.
Tactics, Techniques, and Procedures (TTPs)
- Initial Access: Spear-phishing via email (T1566.002)
- Credential Access: Credential harvesting via web form (T1056 / T1185)
- Defense Evasion: JavaScript-obfuscated/dynamically rendered content; domain rotation; lookalike branding
- Resource Development: Continuous registration of brand-impersonating domains
- Impact: Account takeover followed by secondary fraud (crypto promotion, further phishing)
Indicators of Compromise (IOCs)
Primary domain (active as of 22–23 August 2026)
- contentviolations-x.com (registered 12 August 2026)
Related historical / parallel infrastructure (non-exhaustive)
- flaggedcontents-x.com
- violating-x.com
- policyviolation-x.com
- recognition-x.com
- statuscontent-x.com
- disputes-x.com
- violationsportal-x.com
- Various other *-[alert|notify|access|content]-x.com variants
Email patterns
- Subjects containing “DMCA notice,” “LEGAL-,” “Copyright Violation,” or “content has been reported”
- Claims of account restriction or visibility limitation within 24 hours
Behavioral
- Emails that display the recipient’s own recent X posts as “evidence”
- Landing pages that require password entry solely to “appeal” a copyright claim
Detection and Mitigation Recommendations
- User Education: Legitimate X copyright or DMCA actions never require entering credentials on an external site. Always navigate to x.com directly (bookmark) and check notifications inside the authenticated session.
- Email Filtering: Block or quarantine messages containing -x.com domains in links when the purported sender is X. Monitor for AMP redirect chains that have historically been used to bypass filters.
- Technical Controls:
- Enforce phishing-resistant MFA (passkeys / hardware keys) on high-value X accounts.
- Deploy browser extensions or enterprise secure-browsing solutions that detect newly registered lookalike domains and JS-heavy credential forms.
- Monitor DNS for new *-x.com registrations matching known patterns.
- Incident Response: If credentials were entered, immediately change the X password from a trusted device, revoke all sessions, enable additional 2FA methods, and review connected apps. Report the domain to X’s abuse channels and to the registrar.
- Defensive Monitoring: Organizations with high-profile X presence should treat any unsolicited “DMCA” or “copyright violation” email as high-priority phishing until proven otherwise.
Overview
Defenders should treat any external “X copyright / DMCA” notification as hostile by default and prioritize continuous hunting for the *-x.com naming convention. Ongoing collaboration between platform security teams, registrars, and threat-intelligence providers remains essential to disrupt this infrastructure at scale.