OpenAI Engineer Charged With Planting Covert Recorder in Executive Conference Room
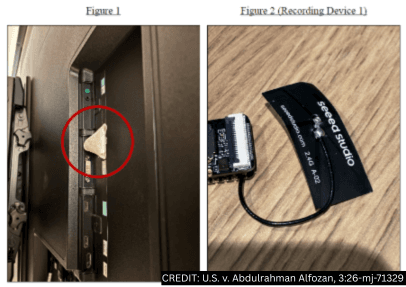
US authorities have arrested Abdulrahman Alfozan, a 35-year-old Saudi national and OpenAI engineer, for allegedly hiding an encrypted audio recorder in an executive conference room at OpenAI's San Francisco office. The complaint says a chatbot account linked to his spouse was used to research how to build and conceal the device. He faces up to 5 years in prison and a $250,000 fine.
The US Department of Justice has charged an OpenAI engineer with using, or attempting to use, a device to intercept oral communications.
Abdulrahman Alfozan, 35, a Saudi national, was arrested on 9 October 2026 and made his first appearance in federal court on 13 October.
What the Complaint Alleges
- Device found: on about 30 September, OpenAI staff found an audio recorder plugged into a USB port on the back of a television in an executive conference room in San Francisco. It was wrapped in toilet paper, had been installed around 28 September, and its contents were encrypted.
- CCTV: footage showed Alfozan, an engineer at OpenAI since July 2025, near the room on several dates before the discovery, although he had no authority to access it or attend its meetings. On 5 October he was seen entering the room and looking behind the television.
- Reconnaissance: before 28 September, he allegedly used an internal productivity tool to look up building addresses, meeting rooms and calendars, "leadership and exec" locations, and external partner meetings.
- AI-assisted build: between 24 and 30 September, a chatbot account linked to his spouse, which shared identifiers with his own account, allegedly asked how to "build a continuous audio recorder," customise Wi-Fi connectivity, improve "live listening" and "encrypt the SD card." It also asked about the specific device's custom header and MAC address.
- Second device: on about 5 October, security staff found a bag he had left unattended, containing his wallet, his ID and a second, similar recording device.
The room regularly hosted discussions of proprietary research, product plans, government engagements and commercial relationships.
Penalty
If convicted, Alfozan faces up to 5 years in prison, a $250,000 fine and 3 years of supervised release.
The FBI is investigating, and the case is being prosecuted in the Northern District of California with the National Security Division's Counterintelligence and Export Control Section.
FBI Director Kash Patel called the protection of American super-intelligence innovation one of the bureau's "highest counterintelligence priorities."
Insider Threat Lesson
The case shows the insider threat facing AI labs: physical bugging combined with research done through AI tools.
It also shows that monitoring of employees' internal tool queries and chatbot accounts can surface evidence.
A complaint is only an allegation, and Alfozan is presumed innocent unless proven guilty.