Mudra Loan Impersonation Scam busted, Andhra Pradesh residents targeted
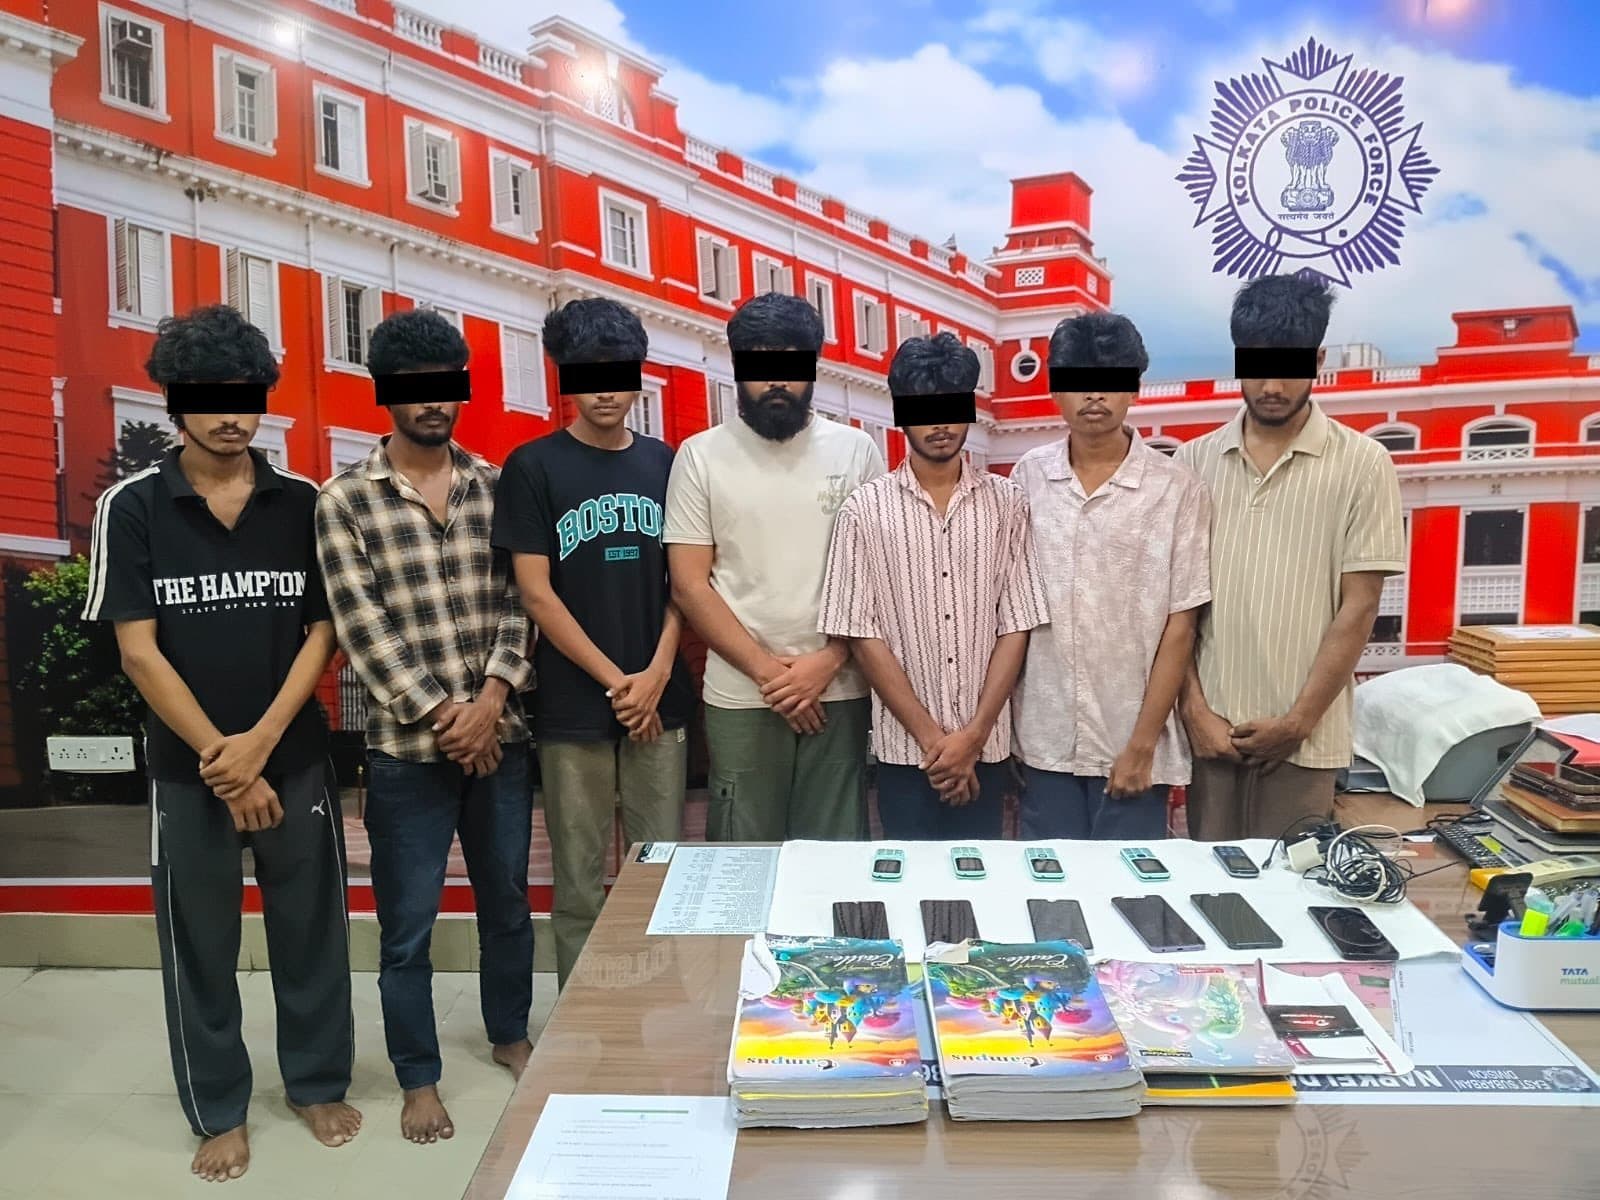
Kolkata Police report that an inquiry into fraudulent SIM procurement uncovered a multi-state cyber-fraud operation. Following the arrest of Taushif Alam on 17 September 2026, officers raided a flat in Hatiara under Eco Park Police Station used as an alleged fraudulent call centre, arresting seven individuals from Andhra Pradesh and Telangana. The accused are alleged to have impersonated MUDRA Loan representatives and induced residents of Andhra Pradesh to transfer funds. Mobile phones and noteb
Kolkata: Kolkata Police have disclosed that an investigation into the fraudulent procurement of SIM cards has exposed a wider multi-state cyber-fraud network, including an alleged fraudulent call centre in Hatiara and a scheme involving impersonation of MUDRA Loan representatives targeting residents of Andhra Pradesh.
Origin of the Investigation
According to the official statement, the inquiry commenced on a report by Sub-Inspector Md. Abbasuddin Biswas of Narkeldanga Police Station, following an enquiry by Cyber Cell, Eastern Suburban Division (ESD).
Investigators allege a conspiracy involving forged documents and SIM cards obtained in the names of various individuals.
Those SIM cards were allegedly supplied to offenders and used in cheating and other cyber-enabled financial crimes.
A significant development occurred with the arrest of Taushif Alam on 17 September 2026.
Interrogation of the accused, police state, led to identification of further suspects and to a subsequent raid on a residential flat in Hatiara under Eco Park Police Station.
Arrests at Alleged Fraudulent Call Centre
Kolkata Police report that seven persons were arrested from the premises, which were being used as a fraudulent call centre.
Items seized, as listed in the official communication, include several mobile telephones and exercise books containing extensive personal data, particularly relating to residents of Andhra Pradesh.
The arrested individuals are described as residents of Andhra Pradesh and Telangana.
They were allegedly brought to Kolkata by Sundar, also known as Ali.
Posing as representatives of a MUDRA Loan company, they are alleged to have contacted persons in Andhra Pradesh and induced them to transfer money into various bank accounts.
Significance of Forged SIM Supply and Loan Impersonation
SIM cards obtained through forged Know Your Customer (KYC) documentation frequently underpin cyber-enabled fraud:
- they obscure caller identity,
- enable rapid number rotation,
- and distance operators from mule accounts.
Combining that infrastructure with impersonation of a recognised government-supported loan brand (MUDRA) constitutes a familiar social-engineering method directed at financially vulnerable targets who may expect official outreach.
Contemporaneous local reporting of the Narkeldanga–Hatiara action is consistent with the forged-document SIM supply chain, the Eco Park / Hatiara raid, and the Andhra–Telangana origin of the accused.
This summary relies on the official Kolkata Police account and does not introduce unstated FIR numbers, charge sections, or quantified financial losses.
Status of the Investigation
Kolkata Police state that a deeper network has been identified and that inquiries are continuing, with a stated commitment to pursue every link in the chain.
Allegations remain subject to investigation and judicial determination.
The public record at present is the official description of forged-KYC SIM procurement supporting a Kolkata-based loan-impersonation operation directed at victims in Andhra Pradesh.