India Unveils 60-Day Cybersecurity Blueprint to Combat AI-Driven Threats to Critical Infrastructure
India’s mandate is clear—if defenders aren’t fighting bots with bots and shrinking remediation from days to mere hours, they are already compromised.
NEW DELHI, In a decisive response to the rapidly evolving landscape of global cyber threats, the Indian government has issued a sweeping directive aimed at fortifying the nation’s digital infrastructure against the escalating risk of artificial intelligence-assisted cyberattacks.
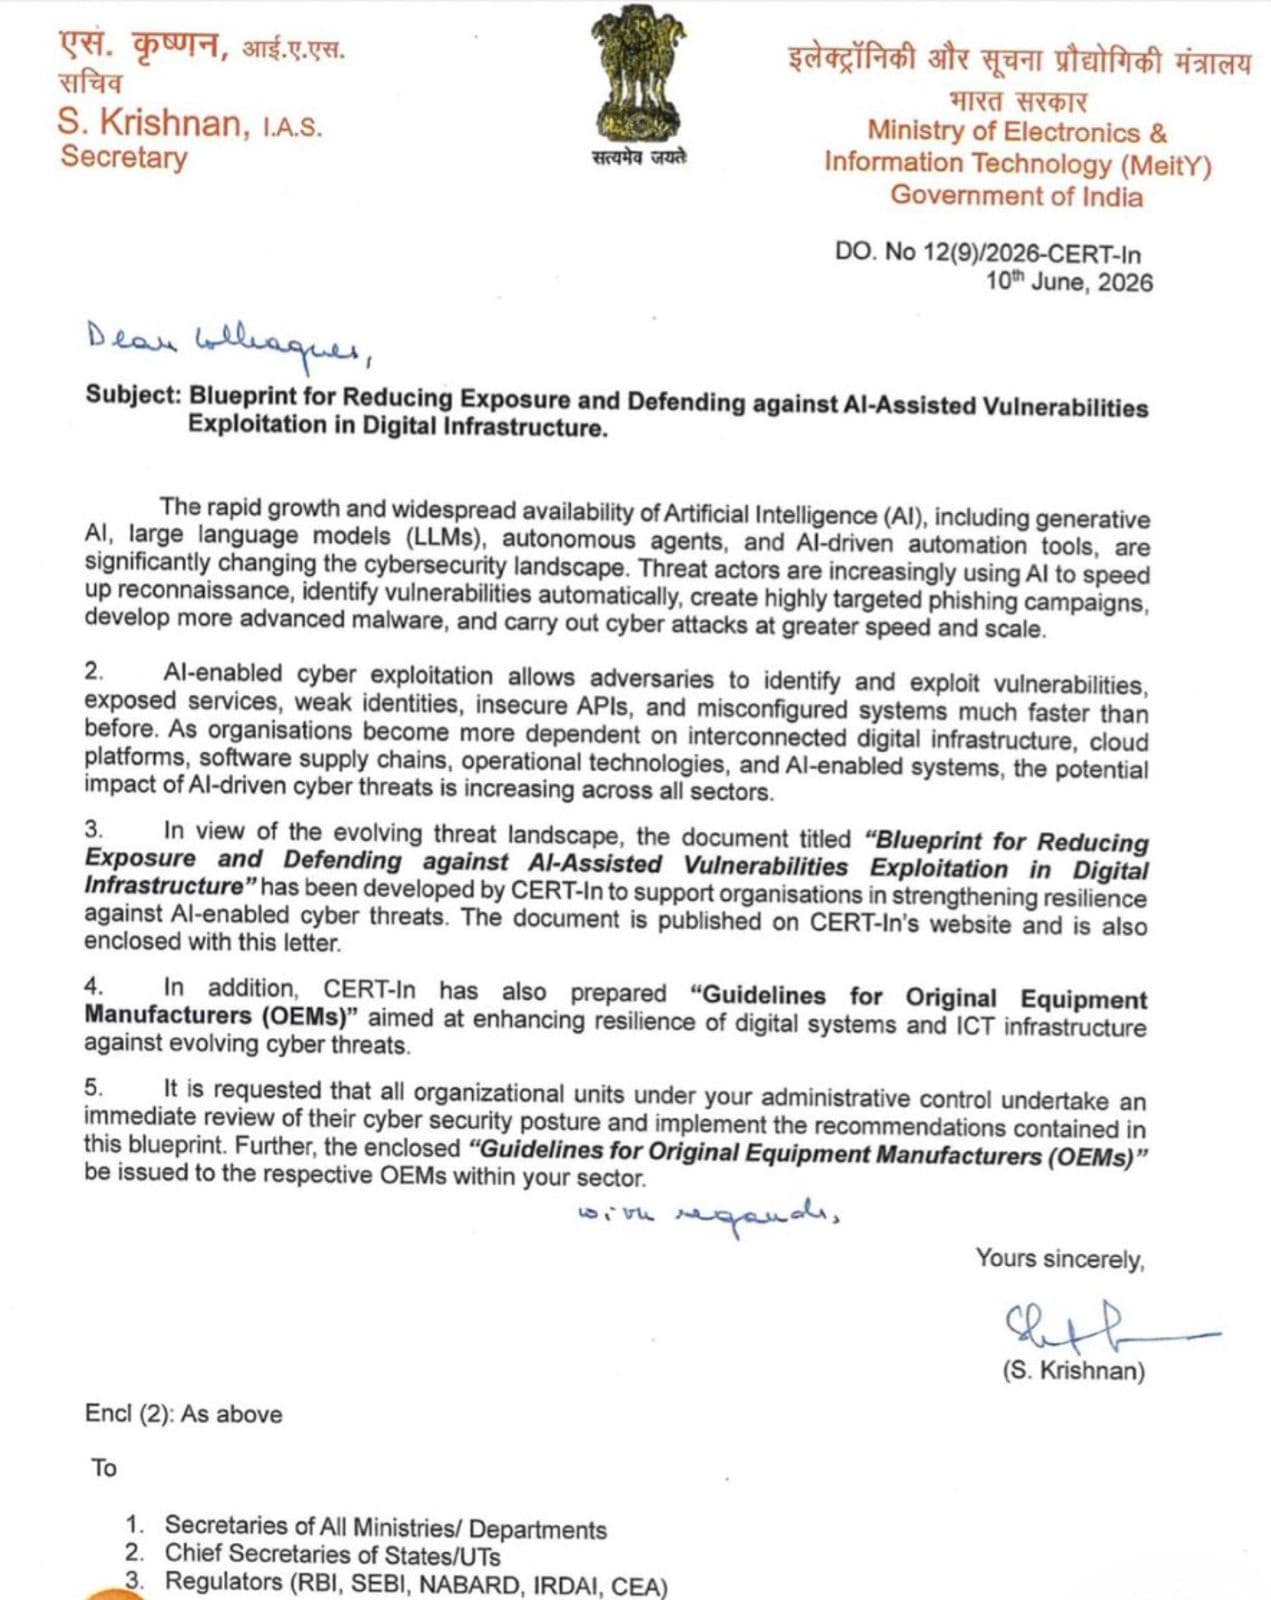
An official communiqué dated June 10, 2026, from the Ministry of Electronics and Information Technology (MeitY), outlines a strategic framework titled the Blueprint for Reducing Exposure and Defending against AI-Assisted Vulnerabilities Exploitation in Digital Infrastructure.
The document, circulated to top-tier government and regulatory bodies, signals a paradigm shift in India's cybersecurity posture, moving from reactive, perimeter-based defense to preemptive, AI-aware resilience.
The directive, addressed to secretaries of all central ministries and departments, chief secretaries of all states, and heads of regulatory bodies, underscores a stark reality: artificial intelligence is fundamentally altering the threat matrix.
The newly released CERT-In blueprint warns that AI technologies, including generative AI, large language models (LLMs), and autonomous agents, are enabling threat actors to automate reconnaissance, weaponize vulnerabilities at machine speed, and launch highly personalized, deepfake-enabled social engineering campaigns.
Central to the government's strategy is a comprehensive 38-page framework developed by the Indian Computer Emergency Response Team (CERT-In).
It mandates a phased, risk-based implementation over the next 60 days, requiring entities to transition from periodic compliance checks to continuous validation and adaptive defense.
The Age of Machine-Speed Warfare:
The blueprint underscores a chilling paradigm shift: the days of human hackers manually probing firewalls are over.
Today’s cyber battlefield is AI versus AI.
With autonomous agents capable of weaponizing vulnerabilities at machine speed, the window for human response has effectively slammed shut.
Key Highlights of the CERT-In Blueprint:
- Aggressive 60-Day Implementation Roadmap: Organizations must adopt a phased approach. Phase I (0-7 days)demands immediate risk reduction, identifying critical assets, enforcing multi-factor authentication (MFA), and patching known exploited vulnerabilities. Phase II (8-30 days) focuses on operational strengthening, including AI governance inventories and behavior-based threat hunting. Phase III (31-60 days) requires advanced resilience testing, such as red teaming and adversarial AI simulations.
- Strict Patch Management Timelines: Reflecting the accelerated speed of AI-driven exploits, the blueprint sets rigid remediation deadlines. Vulnerabilities in internet-facing "crown-jewel" systems that are already being exploited must be contained or patched within 12 hours. Critical external vulnerabilities must be addressed within 1 day, and high-severity vulnerabilities within 5 days.
- Securing the AI Itself: Recognizing that AI systems are not just tools for attackers but also targets, the framework dedicates significant focus to securing enterprise AI. It mandates defenses against prompt injection, model manipulation, and training data poisoning. It also calls for strict governance over "Agentic AI" systems, requiring human oversight, operational boundaries, and emergency shutdown mechanisms for autonomous operations.
- Mandatory Supply Chain Transparency via xBOMs: To secure the digital supply chain, the directive pushes for the widespread adoption of extended Bill of Materials (xBOM) frameworks. Organizations and OEMs are urged to maintain Software (SBOM), AI (AIBOM), Quantum (QBOM), and Cryptographic (CBOM) bills of materials to ensure complete visibility into software dependencies, AI model provenance, and third-party risks.
- "Agentic SOC" and AI-vs-AI Defense: The blueprint calls for the modernization of Security Operations Centers (SOCs) into "Agentic SOCs" that leverage AI-assisted defensive operations. It emphasizes behavioral analytics and anomaly detection, noting that traditional signature-based methods are obsolete against AI-generated malware and adaptive evasion techniques.
- 6-Hour Incident Reporting: Reiterating India's stringent incident reporting norms, the blueprint reminds organizations that cyber incidents must be reported to CERT-In within 6 hours of detection, complete with mechanisms for deepfake detection and AI-specific incident handling.
The MeitY directive makes it clear that traditional static security approaches are no longer sufficient.
As exploitation timelines shrink and attacks become increasingly autonomous, India is mandating a "threat-informed defense" doctrine.
With critical sectors like finance, healthcare, energy, and digital public infrastructure in the crosshairs, the new blueprint asserts that in the modern cyber age, the defense must be as intelligent, adaptive, and rapid as the offense.