India’s Power Grid Gets a Binding Cyber Security Rules : What Changes From April 2027
Binding operational-technology (OT) rules for electricity exist in a handful of jurisdictions. Most of the world still runs plants on vendor advice, IEC 62443 contracts and national CERT circulars. That difference matters. A guideline can be ignored. A reliability standard or a critical-infrastructure statute can shut a control room or fine a board.
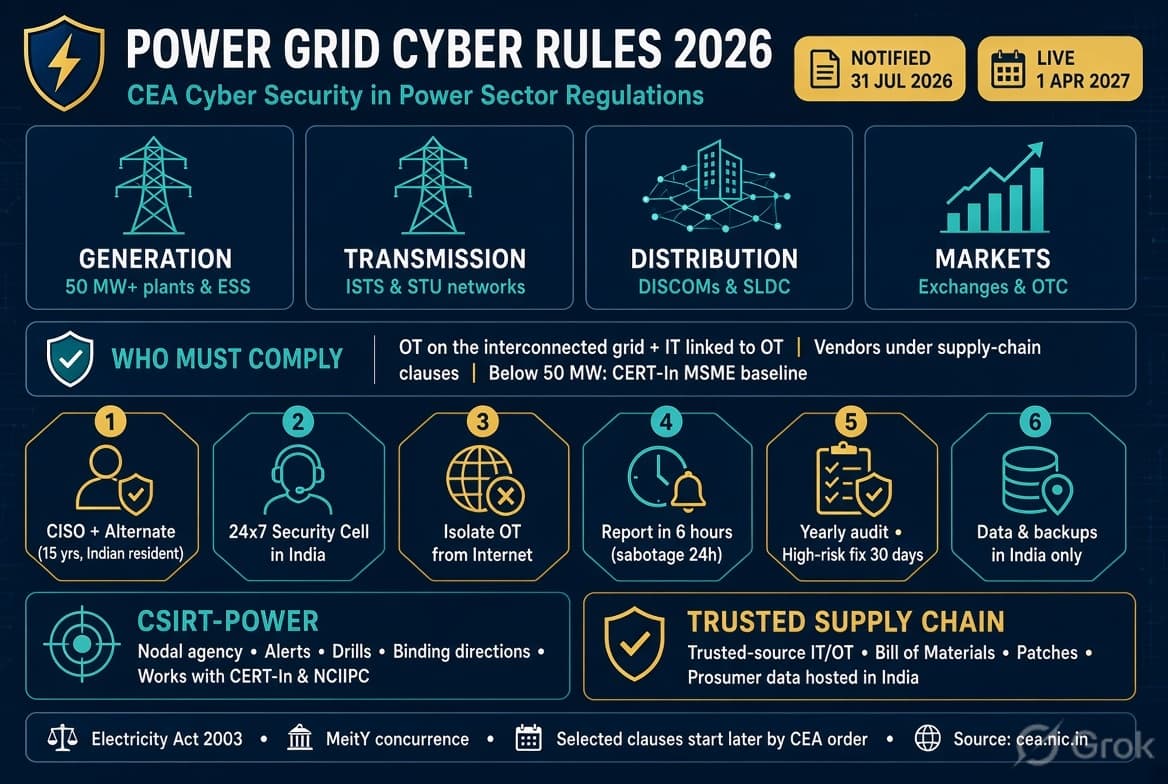
The Central Electricity Authority (CEA) has notified the Central Electricity Authority (Cyber Security in Power Sector) Regulations, 2026, creating binding cybersecurity rules for India’s electricity grid.
Notified: 31 July 2026 Effective: 1 April 2027 Law: Electricity Act, 2003, with MeitY concurrence
This is not a guideline. From next April, large generators, DISCOMs, transmission utilities, load dispatch centres, power exchanges and 50 MW+ storage projects must run named officers, isolate operational technology (OT), store grid data in India, and report cyber incidents within hours.
Who the new CEA cyber rules cover
The rules apply to entities that own, operate or manage:
- OT linked to the interconnected power system
- IT that is physically or logically connected to that OT
In scope: generating companies, captive plants, energy storage systems of 50 MW and above, transmission and distribution licensees, NLDC/RLDC/SLDC, power exchanges and OTC platforms. Vendors supplying equipment and services are covered under specified clauses.
Plants below 50 MW are not fully bound. CEA says they should follow CERT-In’s baseline cybersecurity controls for MSMEs.
Key mandates at a glance
- Appoint a CISO and alternate CISO (Indian citizen and resident, engineering degree, 15+ years in power or IT, minimum 3-year tenure)
- Set up a 24×7 Information Security Division in India
- Keep OT and critical systems off the public internet
- Report incidents to CSIRT-Power and CERT-In within 6 hours
- Report cyber sabotage of critical systems within 24 hours
- Run a yearly cybersecurity audit; close high-risk findings in 1 month
- Store sensitive operational data and backups encrypted, in India
- Buy IT/OT gear from trusted sources and demand a bill of materials
Some of those duties, the 24×7 cell, ISO/IEC 27001 or Technical Criteria Certificate, mandatory training, trusted-source procurement and OT perimeter devices, start later, on dates CEA will notify separately.
CSIRT-Power is now the sector’s cyber desk
Computer Security Incident Response Team – Power (CSIRT-Power), set up in 2023 under the Ministry of Power, is the nodal agency for power-sector incidents. It will issue alerts, set sub-sector benchmarks, run drills and can demand network maps, asset lists, logs and forensics. Its directions bind entities and vendors. CEA can also name sub-sector CSIRTs for generation, transmission, distribution and grid operation.
OT isolation and remote access get hard limits
Critical OT must be physically separated from the internet and from general IT. Remote access is only for troubleshooting and emergencies. Remote operation of OT, if allowed at all, must:
- have head-of-entity or board approval
- run from inside India
- use a dedicated channel isolated from the internet
That hits a common vendor model: OEM engineers patching Indian plants over foreign VPNs.
Audits, patches and cloud data
New critical systems need a cybersecurity audit, including VAPT, before go-live. Web apps go live only after audit clearance. Comprehensive audits must repeat every financial year, with a 9–15 month gap.
Fix timelines after audit:
Finding | Deadline |
|---|---|
Critical / high risk | 1 month |
Medium / low risk | 3 months |
Sensitive grid data, including data on cloud platforms, must stay in India. For prosumer rooftop solar and small storage, vendors must host monitoring, control and historical data in India and encrypt links to DISCOMs and aggregators. Existing rooftop fleets get a later start date.
Why it matters for solar, wind and BESS
Utility-scale renewables and battery projects of 50 MW+ now sit under the same cyber regime as a thermal plant. Cybersecurity becomes a board item: CISO, crisis plan, six-month risk reviews, Indian hosting, trusted hardware.
That is the point. Inverters, BESS EMS and SCADA are now attack surface, not just plant kit. A parallel government push is also asking CEA for a roadmap to stop importing critical SCADA after 2030.
What is still missing
The Gazette does not publish a standalone penalty table. Enforcement will ride on the Electricity Act, licence conditions, CSIRT-Power directions and overlapping IT Act / CERT-In rules. Workforce is the other pinch: the CISO profile is narrow, and brownfield OT isolation is expensive. The staggered start dates are CEA’s way of admitting that.
Bottom line
India has turned power-sector cybersecurity from advice into regulation. 1 April 2027 is the main switch-on. Entities that already have a CISO, OT zoning and Indian data residency are ahead. Everyone else has seven months to stop treating SCADA security as an IT footnote.