CISF Foils IIT Goa Recruitment Cheating Bid: Bluetooth Kits Caught in Airport X-Ray
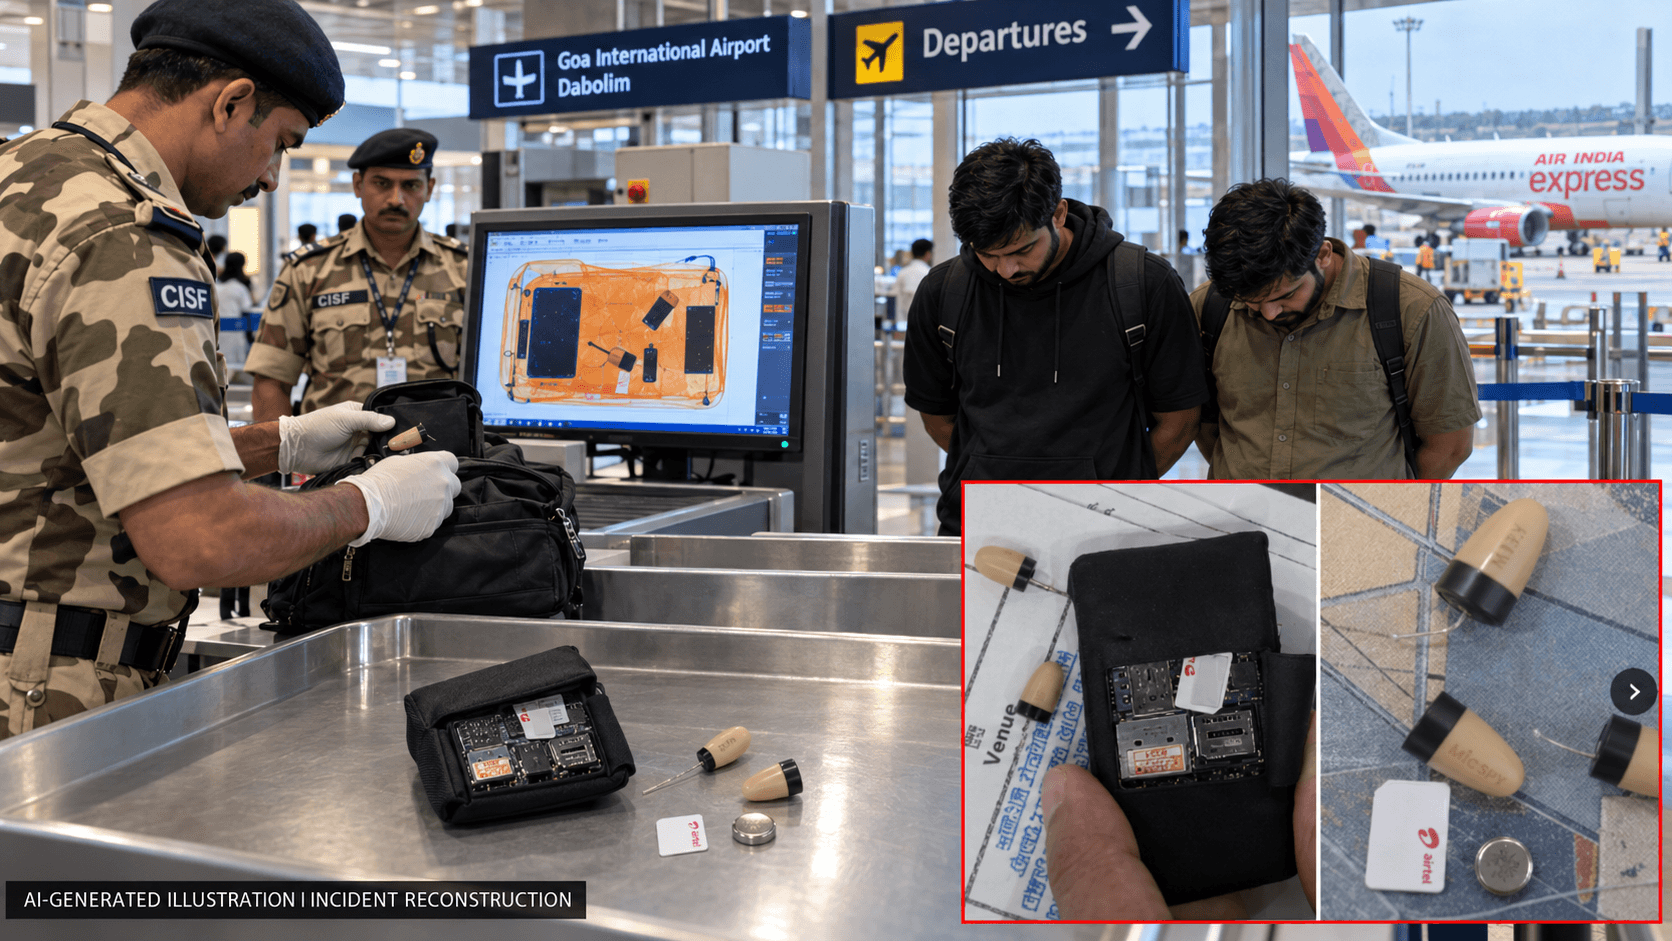
CISF screeners at Goa's Dabolim airport intercepted two Delhi-bound passengers carrying concealed Bluetooth cheating kits linked to the IIT Goa Non-Teaching Staff Recruitment exam. One admitted he had sat the exam in place of another candidate. Both were handed to police and a case has been registered.
Central Industrial Security Force (CISF) personnel at Goa International Airport, Dabolim, intercepted two passengers on 10 October 2026 carrying concealed Bluetooth devices meant for cheating in competitive examinations.
At about 14:25, the first passenger, booked on Air India Express IX-1340 to Delhi, put his handbag through X-ray at the pre-embarkation checkpoint.
The screener flagged suspicious objects, and a physical search turned up three electronic devices, two SIM cards and three Bluetooth earpieces.
Under questioning, he admitted the kit was for exam cheating and said an associate had already boarded the same flight.
CISF had the second passenger offloaded with the help of airline staff.
His bag held a similar device, two Bluetooth earpieces, one SIM card and an admit card for the Administrative Assistant post in the IIT Goa Non-Teaching Staff Recruitment exam held earlier that day.
Impersonation Uncovered
In a joint interrogation with intelligence agencies, the first passenger disclosed that he had taken the exam in place of another candidate.
Aadhaar cards belonging to two other people, which he had thrown away in the security hold area, were recovered.
His claim to be a civilian employee of a defence establishment was verified with the authorities concerned.
Modus Operandi: Bluetooth Relay
- SIM-enabled device: a small unit with its own SIM card, hidden on the body, keeps a live call open to an outside helper.
- Bluetooth earpiece: a tiny earpiece placed deep in the ear receives the answers, and it is hard to spot at a visual check.
- Proxy candidate: an impersonator sits the exam on someone else's identity documents.
- Spare kits: extra devices, SIMs and earpieces point to an organised operation working across multiple candidates or exams.
Action Taken
Both men and the seized items were handed to Dabolim Airport Police and then transferred to Ponda Police Station, which covers the exam centre.
A case has been registered and the investigation continues.
The X-ray screening that caught the kits stopped two suspects in an alleged recruitment fraud from leaving the State with the evidence.