Bitget Hot Wallet Hack: SlowMist Finds Zero-Day Breach and Custom Withdrawal Tool as MetaMask Flags Infrastructure Incident
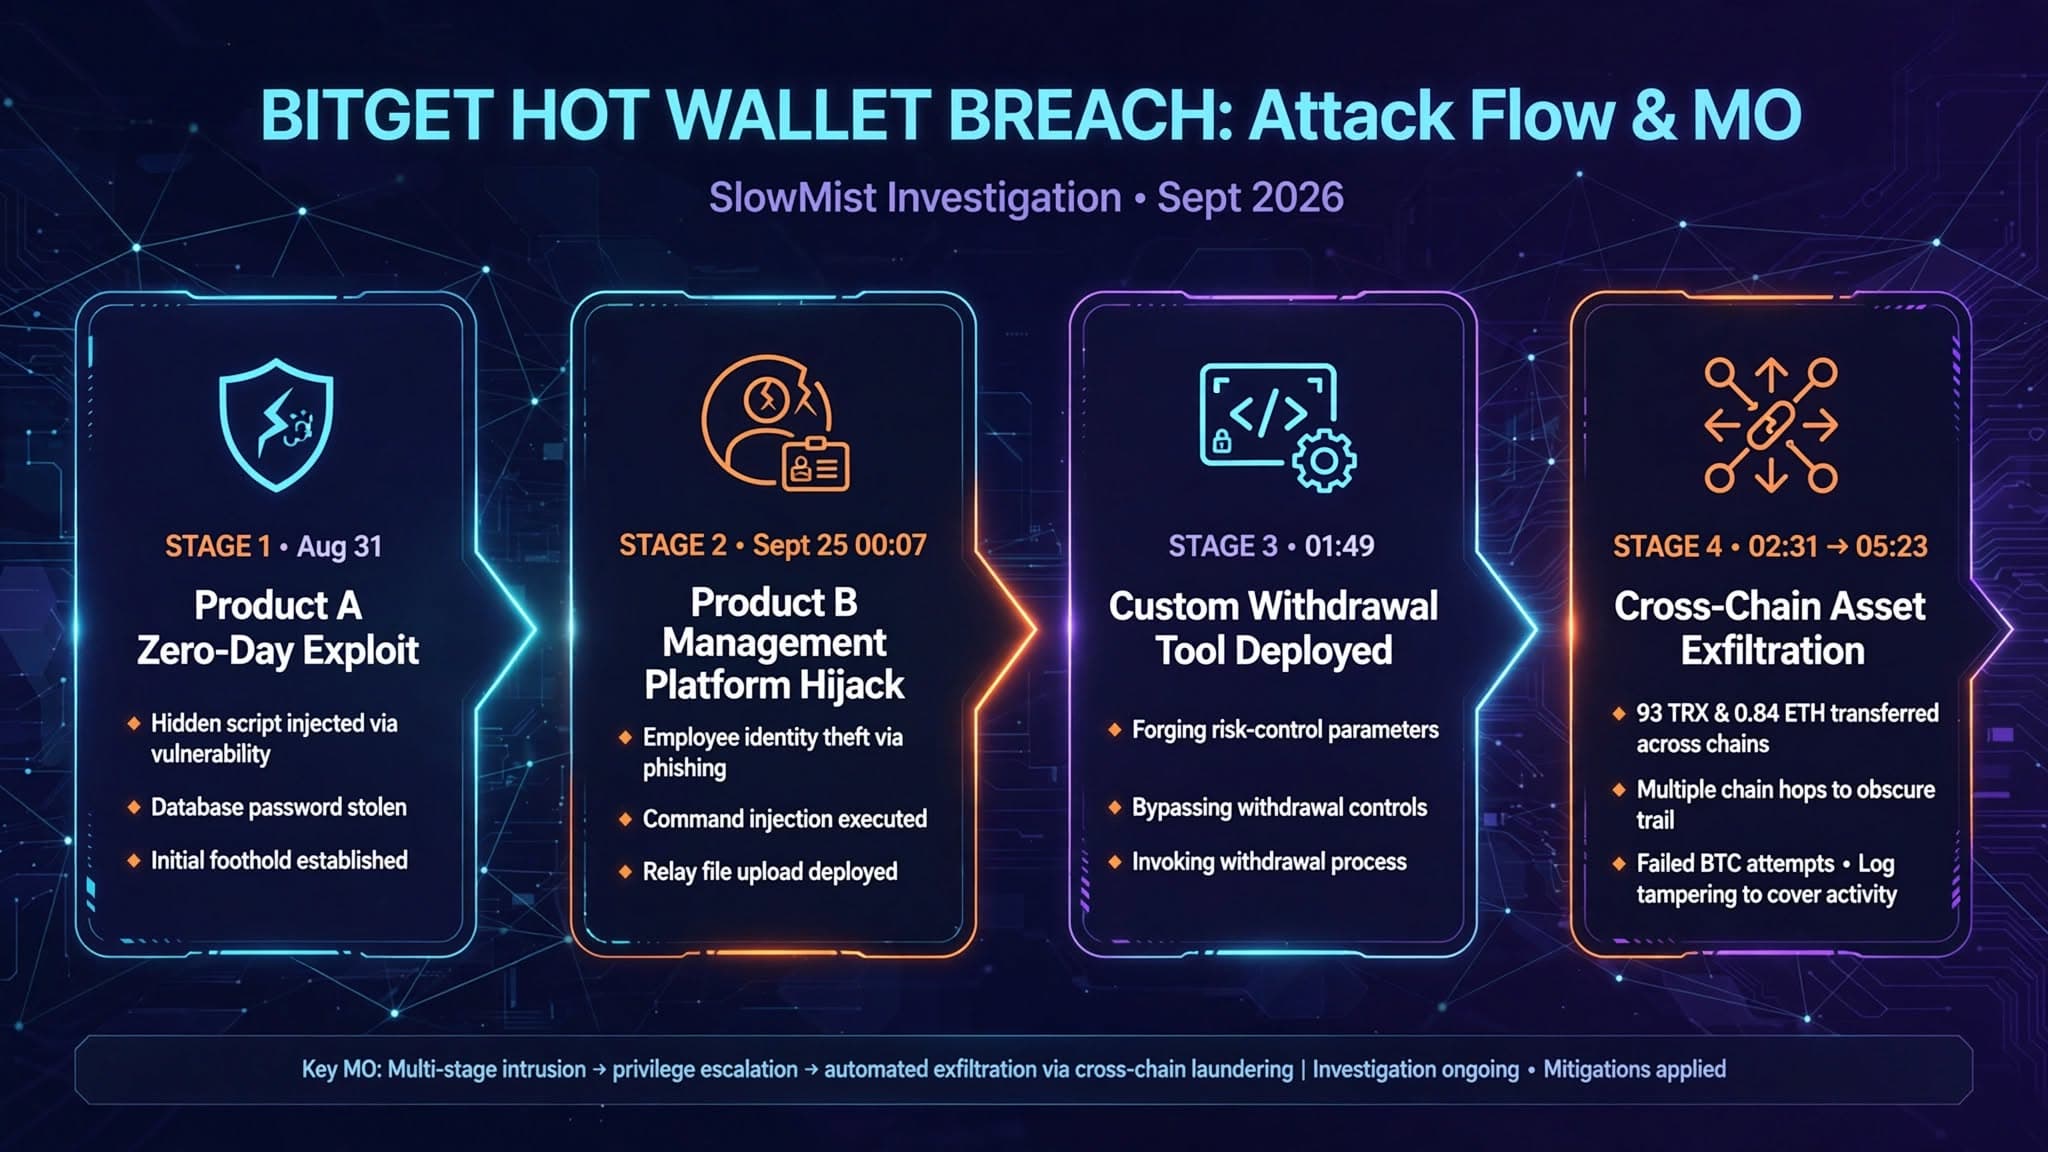
SlowMist’s Bitget IR progress report (as of 29 Sep): Product A 0-day from 31 Aug, Product B admin abuse on 25 Sep, custom withdrawal tool forging risk controls, multi-chain drain ~2h52m from 02:31 UTC+8, later forged BTC withdrawal attempts. Private keys/cold wallets reportedly not compromised.
On September 25, 2026, crypto exchange Bitget invited blockchain security firm SlowMist to investigate the theft of assets from its hot wallets. In a progress report dated September 29, SlowMist said it has already identified malicious activity involving two third-party security products, anonymized as Product A and Product B, and a wallet application host.
The report, marked as of September 29, states investigators have also recovered a highly customized withdrawal tool the attacker built specifically for Bitget's wallet system. All times in the report are UTC+8.
SlowMist Key Findings: Zero-Day to Database Access
According to the investigation, the compromise started well before funds moved.
1. Product A zero-day exploited since August 31:
The earliest malicious activity found in logs dates to August 31. A service running on one of Product A's nodes was hit with a zero-day vulnerability. The attacker ran a hidden script under the service process, read an environment variable containing a database password, and connected to the database. Similar hidden-script activity was seen on two other nodes on September 23 and September 25. SlowMist concludes the service environments were already compromised before any assets were transferred.
2. Product B management platform hijacked on September 25:
In the early hours of September 25, the attacker accessed Product B's management platform using an internal employee's identity. Starting at 00:07, the attacker made three consecutive attempts to inject system commands into task parameters to write malicious files, then used the platform's web execution endpoint to modify server configuration, drop a communication relay file, and upload and assemble malicious program files in batches.
3. The Custom Withdrawal Tool:
Investigators recovered the tool from files the attacker had deleted. Unlike generic drainers, it was tailored to Bitget's withdrawal logic, it forged risk-control parameters in code, constructed withdrawal requests, and invoked the withdrawal process directly. Host logs show the malicious program started executing theft at 01:49 on September 25.
On-Chain Timeline: 2 Hours, 52 Minutes Across Chains
On-chain verification shows the theft began at 02:31:00 on September 25, when the attacker's address received 93 TRX. Eleven seconds later, an Ethereum receiving address got 0.84 ETH. Transfers continued until 05:23:11 that day, spanning nearly 3 hours across multiple blockchains.
After the initial sweep, the attacker tried to cover tracks and push more funds by directly modifying withdrawal records in the wallet database and invoking withdrawal tasks on the local host. Two fabricated BTC withdrawal orders entered processing and returned errors after 05:22, followed by log review and order-status queries.
MetaMask Security Update Today: Separate Alert, Similar Pattern
Hours after the SlowMist report began circulating, MetaMask posted a Security Update on Oct 1, 2026 at 5:08 AM:
"We are responding to a security incident affecting part of our infrastructure. At this time, we have identified no immediate threat to MetaMask wallets. As a precaution, we are proactively exiting affected validators within our non-custodial staking operations, in coordination with clients, partners and security advisors."
The wallet provider said it will share further updates as appropriate. The post has already drawn over 305K views.
While MetaMask describes a validator-level infrastructure issue and Bitget's case involves third-party security products and hot wallets, both incidents highlight a growing trend in 2026 crypto hacks: targeting security infrastructure and staking operations rather than wallets directly.
No official link has been established between the Bitget investigation and the MetaMask incident. There is no confirmation that the same products, validators, or threat actor are involved. The timing has, however, put the industry on high alert for supply-chain and third-party security product vulnerabilities.
What's Next
SlowMist says it is continuing to investigate how the attacker pivoted between systems. The anonymization of Product A and Product B suggests disclosure is still in progress with vendors.
For users and exchanges, the key takeaways remain:
- monitor third-party security tooling for zero-days,
- enforce strict isolation for hot wallet signing hosts,
- and treat environment variables with database credentials as high-value secrets.
This is a developing story. Bitget has not yet released a final loss figure.