"Adception": Google search ads route through Bing to a fake Claude for Mac installer
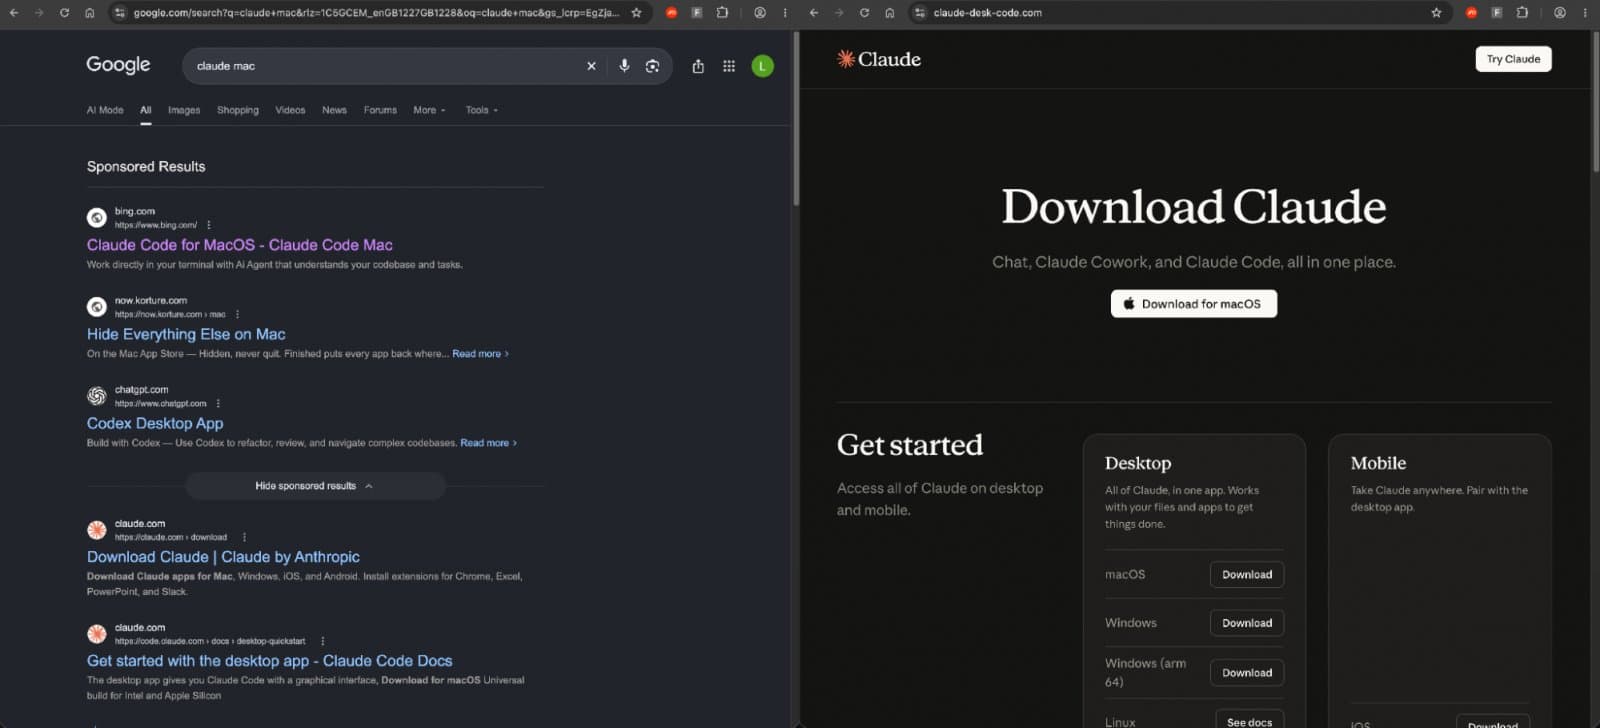
Attackers are running Google search ads for "claude mac" whose destination is a genuine Bing search result. The chain passes through a compromised retail site to a fake Claude download page that copies a malicious terminal command to the clipboard. Push Security calls the technique "Adception": it slips past Google's ad review and link scanners by showing them only trusted domains, and serves the payload only to victims who arrive through the exact path.
A new malvertising campaign is abusing one search engine to hide inside another.
Push Security has detected Google search ads for "claude mac" that send users through a real Bing search result to a fake download page for Anthropic's Claude AI app.
Push has named the technique "Adception."
How the chain works
The sponsored Google result showed bing.com as its domain, not a Claude lookalike.
Clicking it triggered four steps:
- Google's ad-click redirect (google.com/aclk)
- Bing's own search-result redirect (bing.com/ck/a), which forwards the browser with JavaScript and passes on a bing.com referrer
- A compromised but genuine retailer's "about us" page, which forwards only visitors arriving from Bing
- The fake Claude page at claude-desk-code[.]com
Because the ad's destination was simply another search engine, Google's ad review approved it.
The attacker had taken a real, indexed Bing result for a page they had compromised and placed it inside the Google ad.
Two layers of cloaking
The compromised site checks for a Bing referrer and specific browser headers before forwarding anyone.
The fake Claude page then runs a second check in JavaScript: any visitor whose referrer isn't Google or Bing is sent to a 404 page.
Security scanners, ad reviewers and researchers visiting the URL directly see nothing malicious.
The clipboard trick
The final page is a polished copy of Claude's download page, with a "Download for macOS" button and a one-line terminal install.
This is the "InstallFix" variant of the ClickFix social-engineering technique, in which victims are tricked into pasting and running commands themselves.
The page displays Anthropic's real install command, but its Copy button puts a different command on the clipboard.
When pasted into Terminal, it prints "Downloading Claude: https://claude.ai/install.sh" to reassure the user, then quietly decodes a hidden URL and pipes a script from lake-90[.]com into the shell.
Push links the domains to a ClickFix toolkit it tracks as "AcSig."
Why it matters
Redirects through trusted domains are an old evasion trick: Google, Microsoft, LinkedIn and email security link-wrapping services have all been abused this way.
But Push says it found no earlier public report of a search result being used as a search ad's destination.
Push data shows 4 in 5 ClickFix attacks it detects reach victims through search engines.
AI tools are now a favourite lure, because users searching for apps like Claude, ChatGPT and coding assistants are often developers with high-value access.
Indicators of compromise
Push warns that these domains rotate quickly, so IoCs have limited value on their own:
- Google ad campaign ID: gad_campaignid=24303361122
- Lure and delivery domains: claude-desk-code[.]com, ksmgakajgpsals.pages[.]dev, rapid-craft567[.]com, too.clawddddd[.]com, fine-byte2[.]com, fairpoint29[.]com, turbowave45[.]com, cli-desktop[.]com
- Redirect: homeopatiaalemana[.]com/quienes-somos/
- Payload: lake-90[.]com/curl/inhgup9a/a90fkbqdg8d0mus64oh8dw.dat
What users and defenders should do
- Download AI apps only from the vendor's official site, typed directly or bookmarked, never from a sponsored search result
- Never paste terminal commands copied from a web page without reading what was actually copied
- Treat any "install" page that asks you to run a command in Terminal or PowerShell as suspicious
- Block the listed domains and monitor for shell commands that decode base64 URLs and pipe them into curl
- Use browser-level security controls that inspect the full redirect chain and clipboard activity, not just the first URL