The 5-Pillar Framework: What It Really Takes To Be a Successful Cybercrime Investigator
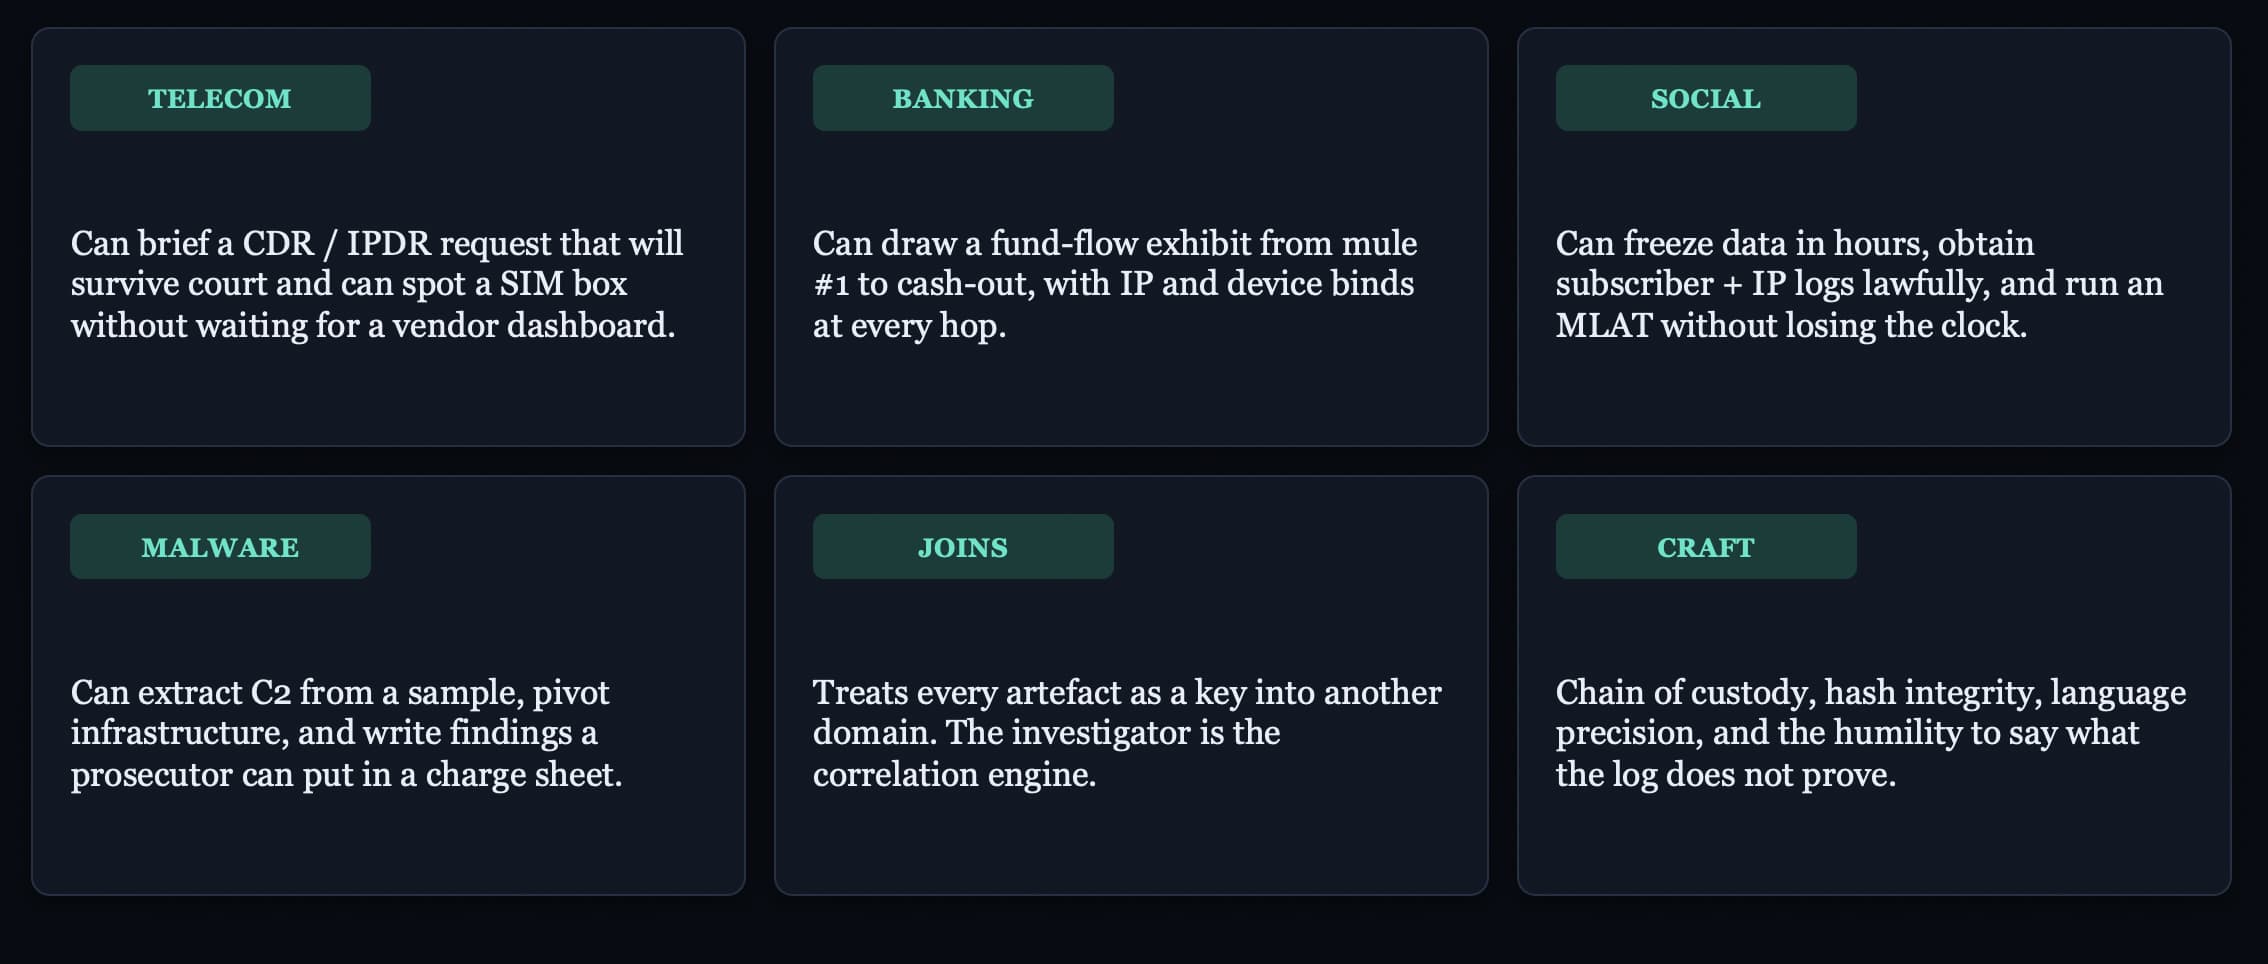
Technology has made cybercrime investigation extremely difficult. A successful investigator needs to master multiple skillset to compete with the criminal's anti-forensic & detection methods
Cybercrime investigation is no longer just about seizing a laptop.
A single case can start with a fake Instagram profile, move through a SIM-box in another state, bounce money through 5 mule accounts and a crypto exchange, and end in a command-and-control server in Eastern Europe.
After working with investigators across India, one pattern is clear - successful investigators are not specialists in one tool.
They are masters of 5 interconnected domains.
Here is the step-by-step blueprint.
PILLAR 1: Telecom Knowledge - Where The Crime Connects
This is your first and most perishable evidence.
Step 1.1: Master CDR & IPDR, Not Just Collect Them
Don't just ask for CDRs.
Ask the right way.
Learn to read: A-party, B-party, IMEI, IMSI, LAC, Cell ID, First/Last LAC.
Plot Cell ID on a map to place the accused at a location.
In IPDR, focus on CGNAT + Private IP + Port + Public IP + Timestamp correlation - without port, you have no user.
Step 1.2: Hunt the Infrastructure, Not Just the Number
SIM Box / GSM Gateway: If you see 500+ calls from a single IMEI with different IMSIs and low ACD (Average Call Duration), it's a SIM Box.
Seize the box, but also get its IP logs - it will lead you to the SIP server.
SIP Lines & VoIP Tracing: Every spoofed call is a SIP.
Get the SIP ID, provider logs, and payment details.
Trace the SIP login IP - most operators use static IPs that never change.
Pro Tip: Always send preservation request to TSP within 24 hours. CDR is available for 1 year, IPDR logs often overwritten in 90 days.
PILLAR 2: Financial Investigation - Follow The Money, It Never Lies
Victims remember the story.
Money remembers the truth.
Step 2.1: Fund Trail Analysis is Layering in Reverse
Create a visual flow chart.
Layer 1: Victim -> Mule 1.
Layer 2: Mule 1 -> 5 accounts in 2 minutes (smurfing).
Layer 3: Consolidation account.
Use lien marking under Section 94 BNSS / 106 BNSS immediately.
Get the account opening form, KYC video, and linked mobile.
Step 2.2: IP Access Logs - The Real KYC
Bank statements tell you what happened.
Bank's IP logs tell you who did it.
Correlate: If Account A and Account B were accessed from the same IP/device ID at 02:13 AM, they are operated by the same person, even if names are different.
Step 2.3: Beyond Domestic
International Payments: For SWIFT / wires, get the MT103 message.
It has the ultimate beneficiary.
Card Transactions: In card fraud, get the payment gateway's MID, TID, and settlement account.
The merchant who settled the money is often the fraudster.
Crypto Trail: This is now mandatory.
Learn blockchain explorers, clustering, and how to write to exchanges.
An address is not anonymous if you can tag it to a KYC exchange with a Law Enforcement Request.
PILLAR 3: Social Media Investigation - Where Evidence Lives on Foreign Servers
Step 3.1: The Correct Legal Workflow
- Preservation First: Email legal@ / lawenforcement@ within hours. Content is deleted in 90 days.
- Lawful Disclosure: Don't ask for "all data". Ask specifically: Basic Subscriber Info, IP logs with timestamps in UTC, login history, connected email/phone.
- Log Analysis: A single Facebook login from IP 103.x.x.x at 14:03 UTC is more valuable than 100 screenshots. Convert UTC to IST and correlate with your IPDR.
India has made life easier for its investigators by introducing Sahyog Portal - for data disclosure facilitation for verified law enforcement agencies across India.
Step 3.2: International Data Requests
Understand MLAT vs. LER vs. Direct Request under IT Act.
For Meta, Google, X, Telegram - 90% data comes via direct LER under their LE portal if you draft it correctly.
MLAT is for content, and it takes months - so preserve now.
PILLAR 4: Malware Analysis - Dissect The Weapon
You don't need to be a malware developer.
You need to be a good reader.
Step 4.1: Identify the C2
When you get an APK or .exe, detonate it in a sandbox (Any.Run, Hybrid Analysis, Joe Sandbox).
Look for network traffic.
One outbound connection to 185.234.x.x:8080 after installation is your C2.
Block it, but first - request subscriber details of that IP from hosting provider.
Step 4.2: Reverse Engineering for Investigators
Learn basic static analysis: Strings, permissions, API calls.
If an app asks for READ_SMS + SEND_SMS + BIND_DEVICE_ADMIN and is a "Loan App", it's a stealer.
Extract IOCs - package name, SHA256 hash, C2 domain, Firebase link.
That Firebase link often has the entire victim database open.
PILLAR 5: Detection - OSINT, Where 80% Cases Are Solved Before FIR
The best investigators find the accused before they even start technical analysis.
Step 5.1: Build the Digital Footprint
Take one data point - a mobile number, UPI ID, or email.
Run the OSINT loop: Truecaller -> Username search -> Breach data (HaveIBeenPwned) -> Domain WHOIS -> Google dork site:instagram.com "number".
Most cybercriminals reuse usernames and profile photos.
Step 5.2: Person / Asset Profiling
Use OSINT to build lifestyle.
A person showing rented bank accounts but flaunting Dubai trips on Instagram? That's your money trail.
Document everything with timestamps and URLs - this is admissible under Section 63 of BSA with a 65B certificate for open-source capture.
Step 5.3: Dark Web Monitoring
Search your case's keywords on dark web markets.
Leaked databases are often sold before victims even realize.
That leak can give you the accused's master database.
The Final Checklist: From Skills to Conviction
A great investigator closes the loop:
- Chain of Custody: Hash everything (SHA256) on seizure.
- Correlation: One crime, one timeline. Put CDR time + Bank IP time + Social Media login time on a single chart. The same IP appearing in all three is your case.
- Documentation: Your investigation is only as good as your case diary and 65B (now 63 BSA) certificates.
Technology changes every 3 months.
The 5 pillars don't.
Master telecom, follow the money, compel data lawfully from social media, dissect the malware, and detect through OSINT - and you will be in the top 1% of cybercrime investigators.