LLM Content Farming on Meta Ads : Instagram 'Typing Jobs' Ad Funnels Users Into Ad-Revenue Trap
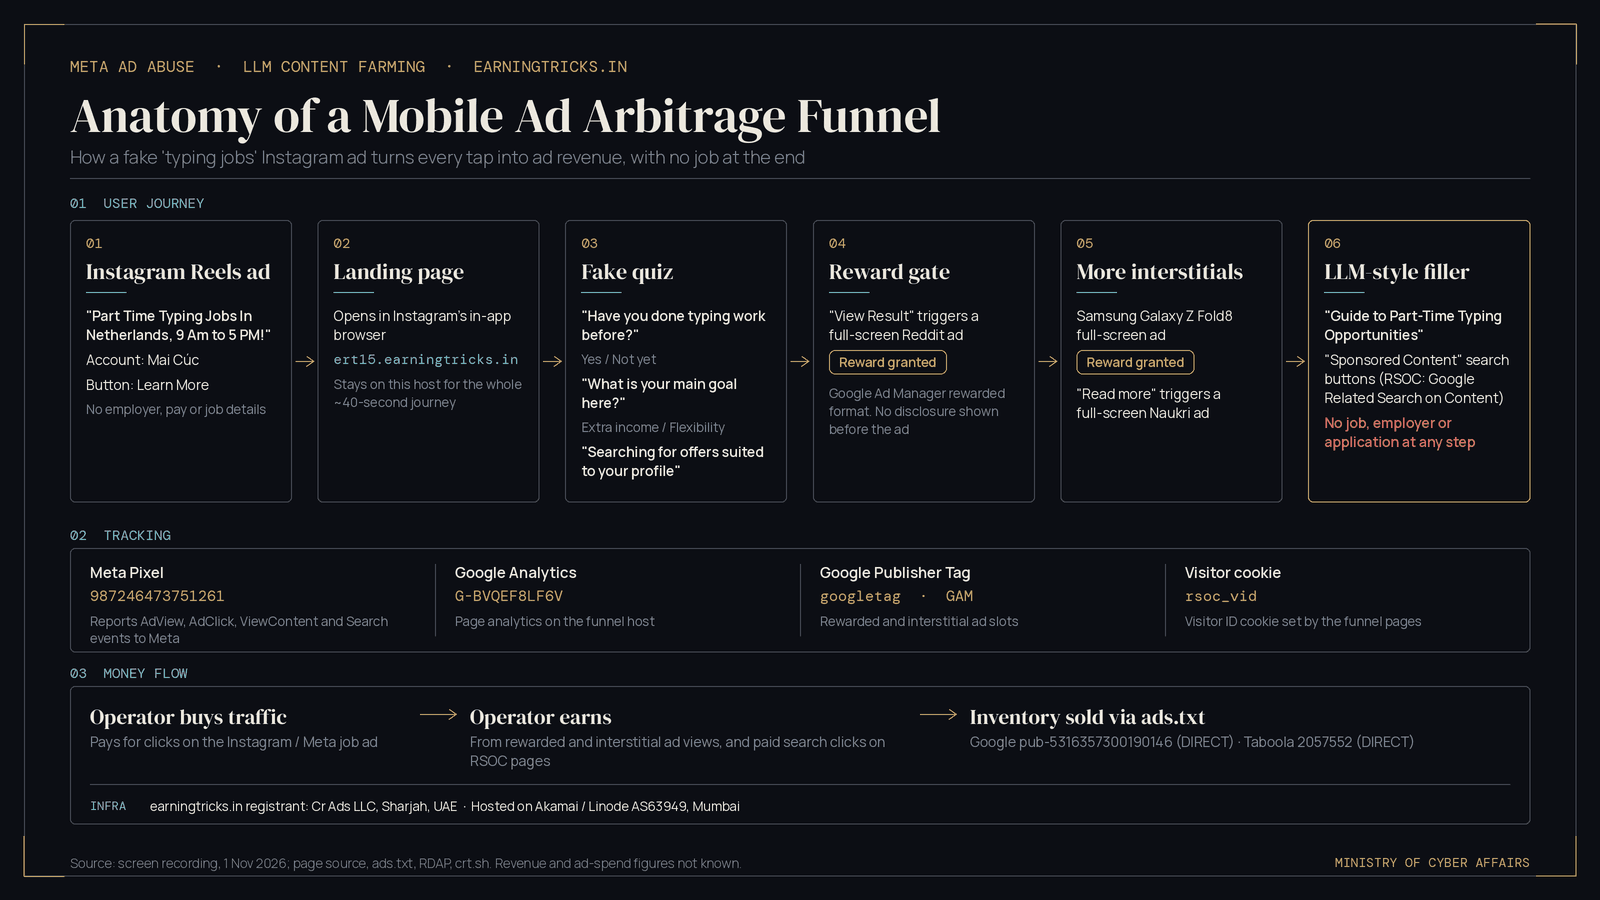
An Instagram Reels ad promising "Part Time Typing Jobs In Netherlands, 9 Am to 5 PM!" sends users to earningtricks.in, where they get a two-question quiz, full-screen "Reward granted" adverts and filler articles with sponsored-search buttons. No employer, job or application ever appears. The site's code shows Google rewarded ad slots, Google related-search (RSOC) buttons and a Meta Pixel that counts ad views and clicks.
An Instagram ad offering "Part Time Typing Jobs In Netherlands, 9 Am to 5 PM!" leads not to an employer but to a chain of full-screen adverts, quiz screens and filler articles. No job, employer or application form appears anywhere in the funnel. A screen recording reviewed by the Ministry of Cyber Affairs shows the journey, and the site's own code shows it is built to earn advertising revenue from every hop.

What the ad promises
The ad ran in Instagram Reels under the account name "Mai Cúc". It shows a woman typing at a laptop beside a window with Dutch-style gabled houses, with the headline "Read More About Part Time Typing Jobs In Netherlands, 9 Am to 5 PM!" and a "Learn More" button. The caption reads: "Are you looking for a flexible way to earn income from the comfort of your own home? Imagine spending your day at a quiet desk, working on typing tasks while enjoying a view of a beautiful European city." The ad names no employer, pay or job details.
How the funnel works
- Tapping "Learn More" opens ert15.earningtricks.in in Instagram's in-app browser.
- A two-question quiz asks "Have you done typing work before?" and "What is your main goal here?" (Extra income or Flexibility). A "Searching for offers suited to your profile" screen follows, then a "View Result" button.
- Tapping "View Result" brings up a full-screen Reddit advert. A "Reward granted" label then appears at the top of the screen. That label belongs to the rewarded ad format in Google Ad Manager, where a viewer watches an ad in exchange for access to content.
- The "result" is a generic article, "Guide to Part-Time Typing Opportunities: An Overview of the Netherlands Market". Below it are blue buttons labelled "Sponsored Content": Typing Careers, Remote Work, Daytime Schedule, Data Entry Opportunities.
- A second full-screen advert, for the Samsung Galaxy Z Fold8, shows another "Reward granted" label.
- A second article, "Overview of Data Entry Opportunities", ends in a "Read more" button that triggers another full-screen advert. This one is a Naukri banner with "Close" and ad-information buttons.
The whole journey took about 40 seconds and stayed on ert15.earningtricks.in throughout.


Who profits
The site's code shows how it makes money. The page served at ert15.earningtricks.in loads Google Publisher Tag (googletag) and refers to "GAM rewarded (#goog_rewarded) and interstitial (#js-read-more)" ad slots. The blue "Sponsored Content" buttons carry the class "js-rsoc". RSOC stands for Related Search on Content, Google's AdSense for Search product. In RSOC, tapping a suggested term opens a search results page full of paid ads, and the site earns money when a visitor clicks one. The site's images are served from a CDN host named contentarb.b-cdn.net.
The two articles in the funnel read like machine-generated filler. Each runs to several hundred words of generic text with no employer, figures or sources, and ends in a string of rhetorical questions. They carry no byline, and each one works as a stop between ads rather than as a guide. This pattern matches LLM content farming, where large language models churn out low-cost pages to hold ad slots. The Ministry's assessment is based on the text itself; the operator has not said how the pages were made.
The page also loads a Meta Pixel (ID 987246473751261) that reports "AdView", "AdClick", "ViewContent" and "Search" events back to Meta. Code comments refer to "rewarded hops". This setup is typical of ad arbitrage: the operator pays Meta for clicks on the job ad and earns more from the adverts and sponsored searches shown on the other side. The Ministry has not seen the operator's revenue or ad spend.
The site's ads.txt file lists Google publisher ID pub-5316357300190146 as a DIRECT seller and Taboola account 2057552 as DIRECT, along with dozens of reseller entries including PubMatic, Index Exchange, OpenX, Magnite (Rubicon), Media.net and Amazon.
What the platforms' rules say
Meta's Prohibited Commercial Practices standard bars job offers that contain "no information about the employer and job specifications, simply referencing job vacancies". Its Unacceptable Business Practices ad policy bars deceptive or misleading offers.
Google's policy for ad units that offer rewards requires publishers to give "clear, accurate and conspicuous disclosure of the action(s) required and reward(s) offered" before each rewarded ad, and to deliver the promised reward. Google's RSOC rules say paid traffic must "accurately describe what the user will see on the destination page" and must not promise offers that are unavailable. In the recording, no screen explained that an ad was about to play or what it would unlock, and no job was ever offered. Whether Google or Meta have reviewed this site has not been confirmed.
Indicators
- Ad account name: Mai Cúc (Instagram Reels ad). The ad could not be checked in Meta's Ad Library.
- Domain: earningtricks.in. Registered 21 February 2019 through GoDaddy and last changed 20 June 2026, per RDAP. The registrant organisation is listed as Cr Ads LLC, Sharjah, United Arab Emirates. The site footer reads "owned by CR Ads LLC".
- Funnel subdomain: ert15.earningtricks.in (172.236.160.100). Certificate Transparency logs also show ert13 and ert14, plus other subdomains including games, arcade, coupons, deals, news and tournament.
- Hosting: 172.236.176.85 and 172.236.176.109 (root domain), Akamai Connected Cloud (Linode), AS63949, Mumbai. DNS is run by Bunny.net (kiki.bunny.net, coco.bunny.net).
- Tracking: Meta Pixel 987246473751261, Google Analytics G-BVQEF8LF6V, visitor cookie "rsoc_vid".
- Ad accounts in ads.txt: Google pub-5316357300190146 (DIRECT), Taboola 2057552 (DIRECT).
Advice for job seekers
- A genuine job ad names the employer, the role, the pay and how to apply. Be wary of ads that say only "part-time typing jobs".
- Quizzes that promise to match you with "offers suited to your profile", followed by full-screen adverts, are a sign of an ad farm, not a recruiter.
- Never pay a fee or share ID, bank or OTP details for a job you found through a social media ad.
- Check vacancies on the employer's own website or on established job portals.
- Report misleading ads on Instagram through the ad's menu (Report ad). In India, report cyber fraud on 1930 or at cybercrime.gov.in.
Sources: screen recording of the ad and funnel; RDAP record for earningtricks.in; crt.sh Certificate Transparency logs; earningtricks.in/ads.txt and page source as fetched on 1 November 2026; Google Ad Manager Help, "Traffic rewarded ads for web"; Google AdSense Help, "Policies for ad units that offer rewards" and "Related search for your content pages"; Meta Transparency Center, "Prohibited Commercial Practices" and "Unacceptable Business Practices".