How Chinese Battery Apps Could Remotely Stop a Moving E-Rickshaw — and Why India Pulled Them
Freely downloadable Bluetooth battery apps let strangers cut power to moving e-rickshaws in India. How the flaw worked, and why the government ordered them removed.
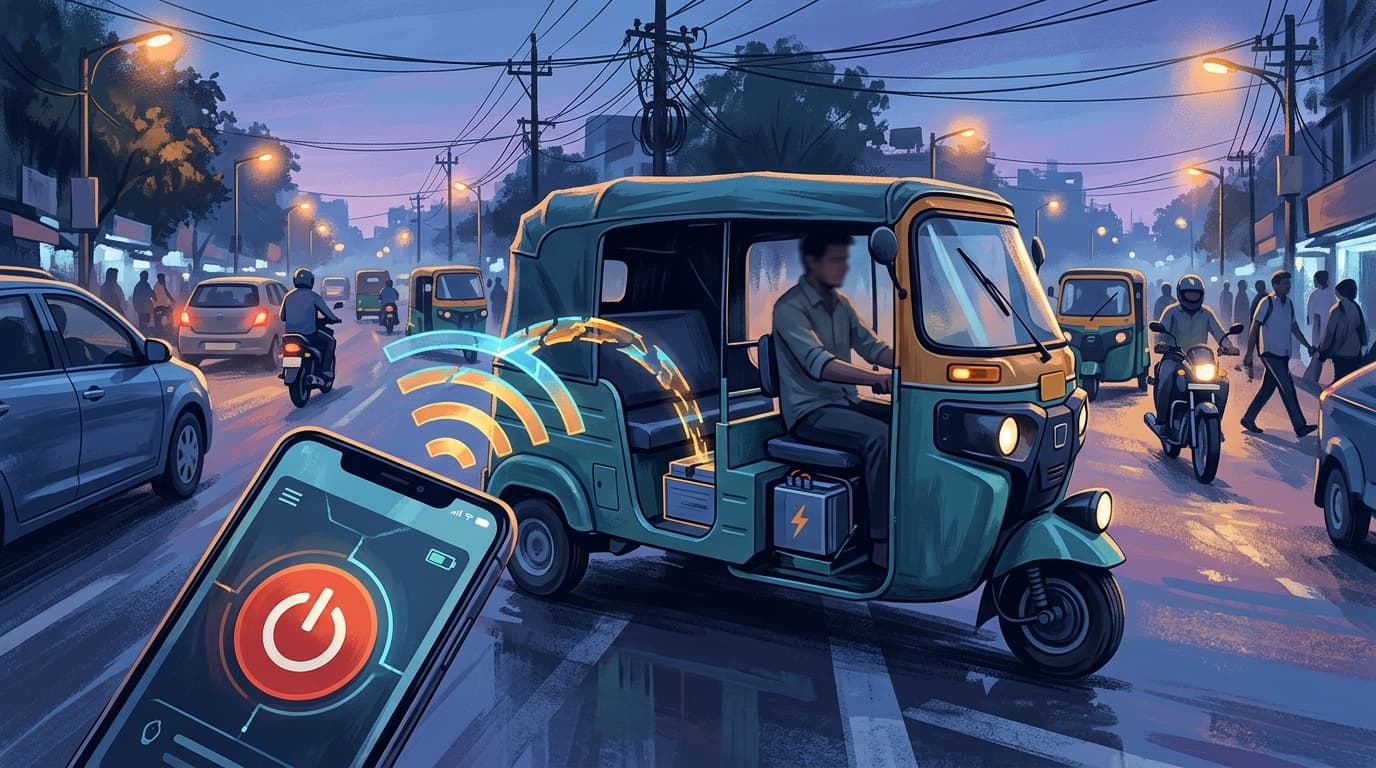
In early July 2026, videos began circulating on Indian social media of a strange, cruel prank: a person walks up to an e-rickshaw, taps something on their phone, and the vehicle simply dies in the middle of the road, its driver left stranded. The trick was real. It worked through freely downloadable battery-management apps, several of them Chinese-made, that could pair over Bluetooth with an e-rickshaw's battery and switch it off. On 3 July 2026, the government stepped in and ordered the apps pulled from the app stores. Here is how the apps worked, how the prank exploited them, and what India actually banned, and did not.
On this page
At a glance
What happened
Speaking at the Confederation of Indian Industry (CII) Cybersecurity Summit on 3 July 2026, MeitY Secretary S. Krishnan confirmed that the government had directed Google and Apple to remove apps from their Indian storefronts after viral clips showed the apps being used to remotely disable e-rickshaws mid-journey. “There are a couple of apps which came to our notice yesterday. Both of them have been taken down from the app stores,” he said, adding that app stores “need to exercise due care” so that “possibly damaging apps don't come up.”
The Secretary named two apps on record, BAT-BMS and Epoch Li-ion. Mainstream reporting added a third, Lossigy, and a subsequent ANI report, citing government sources, put the full direction at up to seven apps, though only three or four have been named publicly. The social-media prank driving the panic was circulating under names like the “Tirri” trend.
How the apps used to work
These are Battery Management System (BMS) apps, and in their intended use they are perfectly legitimate. Many e-rickshaws now run on lithium-ion battery packs fitted with a smart BMS that talks to a phone over Bluetooth. Through an app, an owner or fleet operator can monitor the battery's voltage, temperature, charge cycles and power output, useful for maintenance and for spotting a failing cell before it strands a driver.
Crucially, that same BMS also exposes a control the prank abused: a remote toggle for the battery's discharge circuit, essentially an on/off switch for power delivery. In normal use it lets an owner shut a battery down safely. The apps are ordinary phone apps that anyone can download from the store; they are not embedded manufacturer firmware or locked to a particular vehicle.
The flaw the prank exploited
The vulnerability is not really in the app. It is in the battery hardware. To keep costs down, many low-end e-rickshaw battery packs ship with their Bluetooth interface open, with no default password or authentication. That means anyone standing within roughly 10 to 15 metres, running a compatible BMS app, can pair with the battery and flip the discharge switch, cutting power to a moving vehicle without the driver's knowledge or consent. No hacking skill is required; the app does exactly what it is built to do, just to a battery that was never the user's to control.
The real-world harm
What began as “prank” content quickly stopped being funny. Drivers reported being stranded and losing a day's earnings of several hundred rupees; one had to push his vehicle several kilometres for repairs. Incidents were reported around Delhi University's North Campus, near Jamia Millia Islamia, in Sikandarpur (Gurugram) and in Patna, and at least one arrest was made in Ujjain where the method was allegedly used for extortion. A remote kill-switch on a moving three-wheeler carrying passengers is a road-safety hazard, not a joke, which is precisely the government's stated concern.
Why they were banned (and why not)
It is worth being precise here, because the story is widely misreported. Every on-record government statement gives the same reason: public and road safety, and the immediate misuse of the remote-shutdown feature. That is why the apps were pulled.
What officials did not say is just as important. There is no official statement claiming these apps were secretly siphoning location or route data to Chinese servers, and no stated national-security or surveillance rationale for this action. Some of the apps are indeed Chinese-made, BAT-BMS is developed by Shenzhen Grenergy Technology and Lossigy by Shenzhen RuiChuang Lithium Energy Technology, and it is fair to ask what telemetry any always-connected battery app collects. But that is an open question, not the reason given for the ban. Treating “data going to China” as the official cause would be inaccurate; this was a safety takedown of apps that happened to be Chinese, not a data-espionage ban.
How the ban actually works
This was an administrative direction to the app stores to remove the apps, not a formal blocking order. That is a meaningful distinction from India's 2020 wave of Chinese-app bans (TikTok, UC Browser and dozens more), which were issued under Section 69A of the IT Act on national-security grounds and published as gazette notifications. For the e-rickshaw apps, officials indicated MeitY was still examining whether to invoke Section 69A for a formal block; as of the takedown, the action was a store-level removal, and misuse can separately be prosecuted under IT Act provisions such as Sections 43 and 66. In short: removed from the stores, yes; formally “banned” under 69A like the 2020 apps, not confirmed.
The problem the ban does not fix
Pulling three, or seven, named apps does not close the hole. The root cause is a hardware design flaw: battery packs whose Bluetooth is left unauthenticated. Any other compatible BMS tool, now or in future, could exploit the same open interface, and app stores cannot catch every utility app that talks to a battery. The IT Secretary hinted at this himself, warning app stores more broadly about “potentially damaging apps.” Until battery makers are required to secure the Bluetooth interface with authentication, the underlying vulnerability remains on the road. Note that only e-rickshaws with Bluetooth-enabled lithium-ion BMS packs are affected; older lead-acid vehicles are not.
If you drive or own an e-rickshaw
No official advisory for drivers has been issued, so the following is practical guidance, not a government instruction:
- Ask your battery vendor whether the BMS Bluetooth is password-protected, and insist on a pack that requires a PIN or pairing key. An open, no-password battery is the real risk.
- If your app lets you set a Bluetooth password or disable remote access, do it. Removing the app from your own phone does not protect the battery; securing the pack does.
- Treat a sudden, unexplained power cut as possible interference, not just a fault, especially if strangers are nearby, and report harassment or extortion to the police and at cybercrime.gov.in or the helpline 1930.
- Prefer batteries and controllers from vendors who publish a security standard. As enforcement tightens, unsecured Bluetooth packs are likely to be phased out.
Frequently asked questions
Were these apps banned for spying or sending data to China? No. The government cited public and road safety and the remote-shutdown misuse. Some apps are Chinese-made, but no official statement alleged data exfiltration; that framing is not supported.
Which apps were removed? BAT-BMS and Epoch Li-ion were named on record; Lossigy was added in mainstream reporting; sources cited by ANI put the total at up to seven, most unnamed.
How could a stranger stop my e-rickshaw? By pairing over Bluetooth with a battery pack that has no password and using a BMS app's discharge toggle, from roughly 10 to 15 metres away.
Does removing the app fix the problem? No. The flaw is the battery's unsecured Bluetooth. Any compatible tool could exploit it until the hardware is secured.
Is my e-rickshaw affected? Only if it uses a Bluetooth-enabled lithium-ion battery with a smart BMS. Lead-acid battery vehicles are not affected.
Sources
- MeitY Secretary S. Krishnan, remarks at the CII Cybersecurity Summit, 3 July 2026 (reported by Digit.in, Business Standard, TechXplore).
- Business Standard, “Govt lens on e-rickshaw shutdown issue; apps removed from app stores,” 3 July 2026.
- TechXplore, “India takes down battery apps after stalled e-rickshaw rides,” July 2026.
- ANI (via Newkerala), MeitY direction to Google and Apple covering up to seven apps (sourced).
- Republic World, on BAT-BMS / Shenzhen Grenergy Technology.
- Lossigy official company page and App Store listing (Shenzhen RuiChuang Lithium Energy Technology).
If you have been targeted or harassed using a device like this, you are not alone. See our cybercrime help hub for step-by-step reporting and recovery guides.