Emerging "Boss Scam": How Threat Actors Leverage DLL Sideloading to Hijack WhatsApp Web and Defraud Enterprises
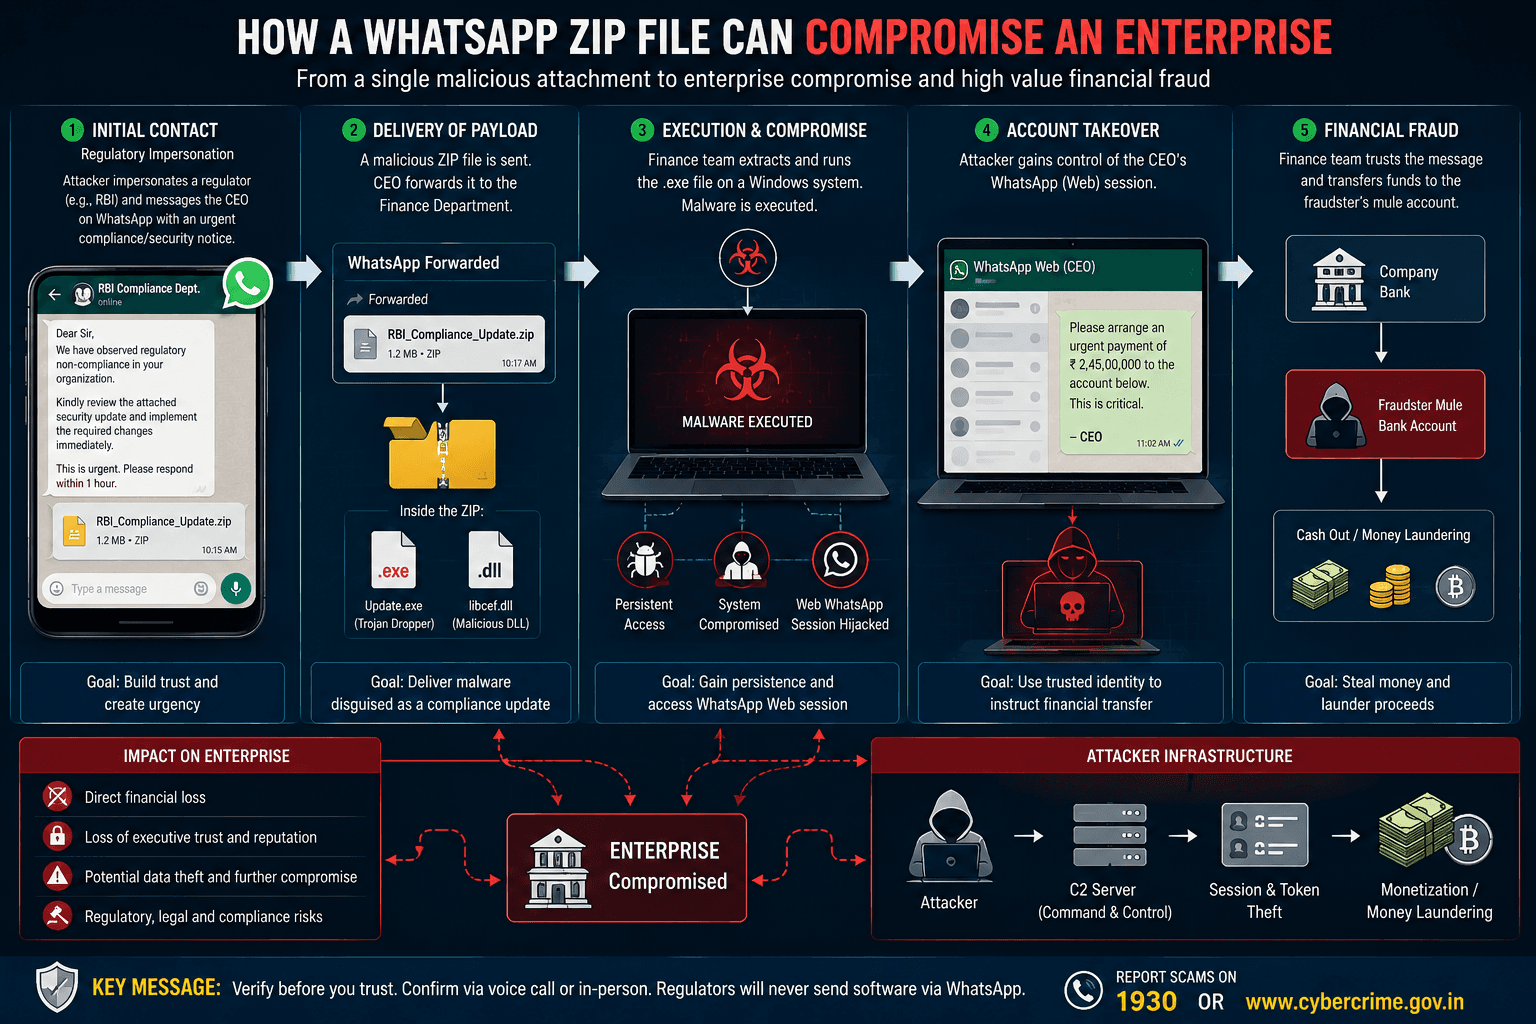
Ministry of Home Affair issues an alert on rising sophesticated boss scam utilizing DLL Sideloading and WhatsApp web compromise. Several high profile cases have been reported with the same MO.
By Cybersecurity Threat Intelligence Desk
In the ever-shifting landscape of cyber threats, Business Email Compromise (BEC) and CEO fraud have long been lucrative staples for financially motivated threat actors. However, a newly detailed campaign demonstrates a sophisticated evolution of this tactic, merging advanced social engineering with technical exploitation, specifically Windows DLL sideloading and WhatsApp Web session hijacking.
A recent advisory from the National Cybercrime Threat Analytics Unit (NCTAU) under the Indian Cyber Crime Coordination Centre (I4C), Ministry of Home Affairs, sheds light on this emerging threat, codenamed the "Boss Scam." This campaign marks a dangerous convergence where traditional executive impersonation meets endpoint compromise and messaging platform takeover.
The Attack Chain: From a WhatsApp message to Takeover
The modus operandi of this campaign is an example of a multi-stage cyber kill chain, leveraging both human vulnerability and technical blind spots.
Stage 1: The Regulatory Lure The attack begins with highly targeted social engineering. Threat actors contact C-suite executives or high-ranking officials via email or WhatsApp, impersonating regulatory bodies such as the Reserve Bank of India (RBI). The message fabricates a sense of acute urgency, claiming regulatory violations or mandating immediate security improvements with an artificially tight deadline. In a critical twist observed by I4C, targeted executives, believing the threat to be real, often forward the malicious payload to their finance officers, inadvertently bypassing initial security checkpoints.

Stage 2: Delivery and DLL Sideloading The payload is delivered as a compressed .zip archive. Inside are two crucial components: a malicious executable (.exe) and a Dynamic Link Library (.dll) file.
This is where the campaign demonstrates technical sophistication through DLL Sideloading. Rather than relying solely on the executable to perform malicious actions, which would likely trigger modern Endpoint Detection and Response (EDR) solutions, the malware leverages a known Windows application programming interface (API) vulnerability. When the user extracts and executes the .exe file, it acts as a legitimate-looking loader that actively calls and executes the malicious .dll.
Because Windows applications inherently trust and load DLLs from their current working directory, this sideloading technique allows the Trojan dropper to establish a persistent foothold on the Windows endpoint while evading traditional security filters that might otherwise flag the standalone executable.
Stage 3: WhatsApp Web Session Hijacking Once the endpoint is compromised, the malware's primary objective is not to encrypt files or destroy data, but to silently intercept active communications. The Trojan targets active Web WhatsApp session tokens stored on the compromised Windows machine. By extracting these session cookies or authentication tokens, the attackers effectively clone the executive's WhatsApp Web session. This grants them unfettered access to the executive's ongoing conversations without ever needing to bypass Multi-Factor Authentication (MFA) on the mobile device itself.
Stage 4: The Financial Fraud Armed with a hijacked WhatsApp Web session, the threat actors pivot to the financial fraud phase. Operating from the CEO's compromised account, they issue urgent transfer instructions to subordinate finance employees. The requests, coming from a verified and trusted account, carry high inherent legitimacy, prompting immediate wire transfers to attacker-controlled mule accounts.
In a secondary variant of this attack, if the malware achieves full device takeover, the threat actors covertly manipulate the device's contact list. They save a fraudulent, attacker-controlled phone number under the CEO's name and use this secondary channel to issue transfer instructions, ensuring a fallback mechanism if the Web WhatsApp session is detected and terminated.
Strategic Implications for Enterprise Security
The "Boss Scam" campaign highlights several critical gaps in modern enterprise security postures:
- The Blurring of Personal and Professional Boundaries: The attack exploits the common use of personal messaging applications (like WhatsApp) for sensitive corporate communications, a channel often left unmonitored by enterprise security teams.
- Over-Reliance on Trust-Based Verification: Finance teams frequently process urgent requests from executive accounts based purely on the digital identity (e.g., a WhatsApp profile picture or a known phone number), rather than out-of-band verification.
- Endpoint Blind Spots: The successful use of DLL sideloading indicates that many enterprise endpoints still lack strict application whitelisting or allow unverified executables to run from user-profile directories.
Recommended Mitigations and Defensive Strategies
To defend against this convergence of social engineering and technical malware delivery, organizations must adopt a multi-layered defense strategy:
- Enforce Out-of-Band Verification: Finance departments must institute strict protocols requiring direct voice verification or in-person confirmation for any urgent financial transaction or bank account change, regardless of the originating platform (email or WhatsApp).
- Implement Strict Software Restriction Policies (SRP): System administrators must configure Group Policy to block the execution of unauthorized .exe and .dll files, specifically those originating from untrusted user-profile directories (e.g., Downloads, AppData). This directly mitigates the DLL sideloading technique.
- Harden Messaging Application Hygiene: Enterprises utilizing WhatsApp for business must educate executives to regularly audit their authorized devices. This can be done by navigating to Settings > Linked Devices within the mobile app and proactively logging out of any dormant or unrecognized Web WhatsApp sessions.
- Enhance Endpoint Detection: Ensure all Windows endpoints are equipped with next-generation antivirus (NGAV) and EDR solutions capable of detecting process injection, DLL hijacking, and the unauthorized extraction of browser or application session tokens.
- User Awareness Training: Continuously educate C-suite executives on the reality that legitimate regulatory bodies (such as the RBI) will never distribute mandatory software updates, security patches, or compliance tools via unsolicited WhatsApp attachments or .zip files.
Conclusion
The "Boss Scam" represents a maturation of the CEO fraud playbook. By weaponizing Windows DLL sideloading to hijack WhatsApp Web sessions, threat actors have successfully bypassed traditional email security gateways and exploited the implicit trust placed in messaging platforms. Enterprises must recognize that the perimeter has extended to the executive's endpoint and their personal messaging applications, requiring a swift update to both technical controls and financial verification protocols.
Note: Organizations or individuals who encounter such fraudulent applications or fall victim to this scam are strongly encouraged to report the incident immediately